VulnTracker Blog

Vulnerability intelligence, decoded.

Exploited-in-the-wild alerts, CVE deep-dives and practical guidance for the engineering and security teams who have to ship the fix.

CVE-2025-61624: PEERSTITCH Malware Abuses a FortiOS Path Traversal Flaw
Fortinet · CISA KEV · Active Exploitation · FortiOS · Malware

CVE-2025-61624: PEERSTITCH Malware Abuses a FortiOS Path Traversal Flaw

Fortinet fixed CVE-2025-61624 in April and rated it Medium. In October, CISA added it to KEV after Unit 42 showed it helping deploy PEERSTITCH, a memory-only implant on FortiGate firewalls. Here are the fixed versions and what to hunt for.

7 min read
CVE-2026-99999 (PwnEscape): Linux Kernel Flaw Lets a Guest VM Read Host Memory
Linux · Kernel · PwnEscape · Cloud Security · Vulnerability

CVE-2026-99999 (PwnEscape): Linux Kernel Flaw Lets a Guest VM Read Host Memory

A Linux kernel flaw, CVE-2026-99999 (PwnEscape), lets code inside a guest VM read host memory. It scores 9.3, needs a foothold in a guest, and has no reported exploitation. Fixed kernels are available for every stable branch.

5 min read
Exploited CVEs Last Week: October 5-11, 2026
Active Exploitation · CISA KEV · Weekly Digest

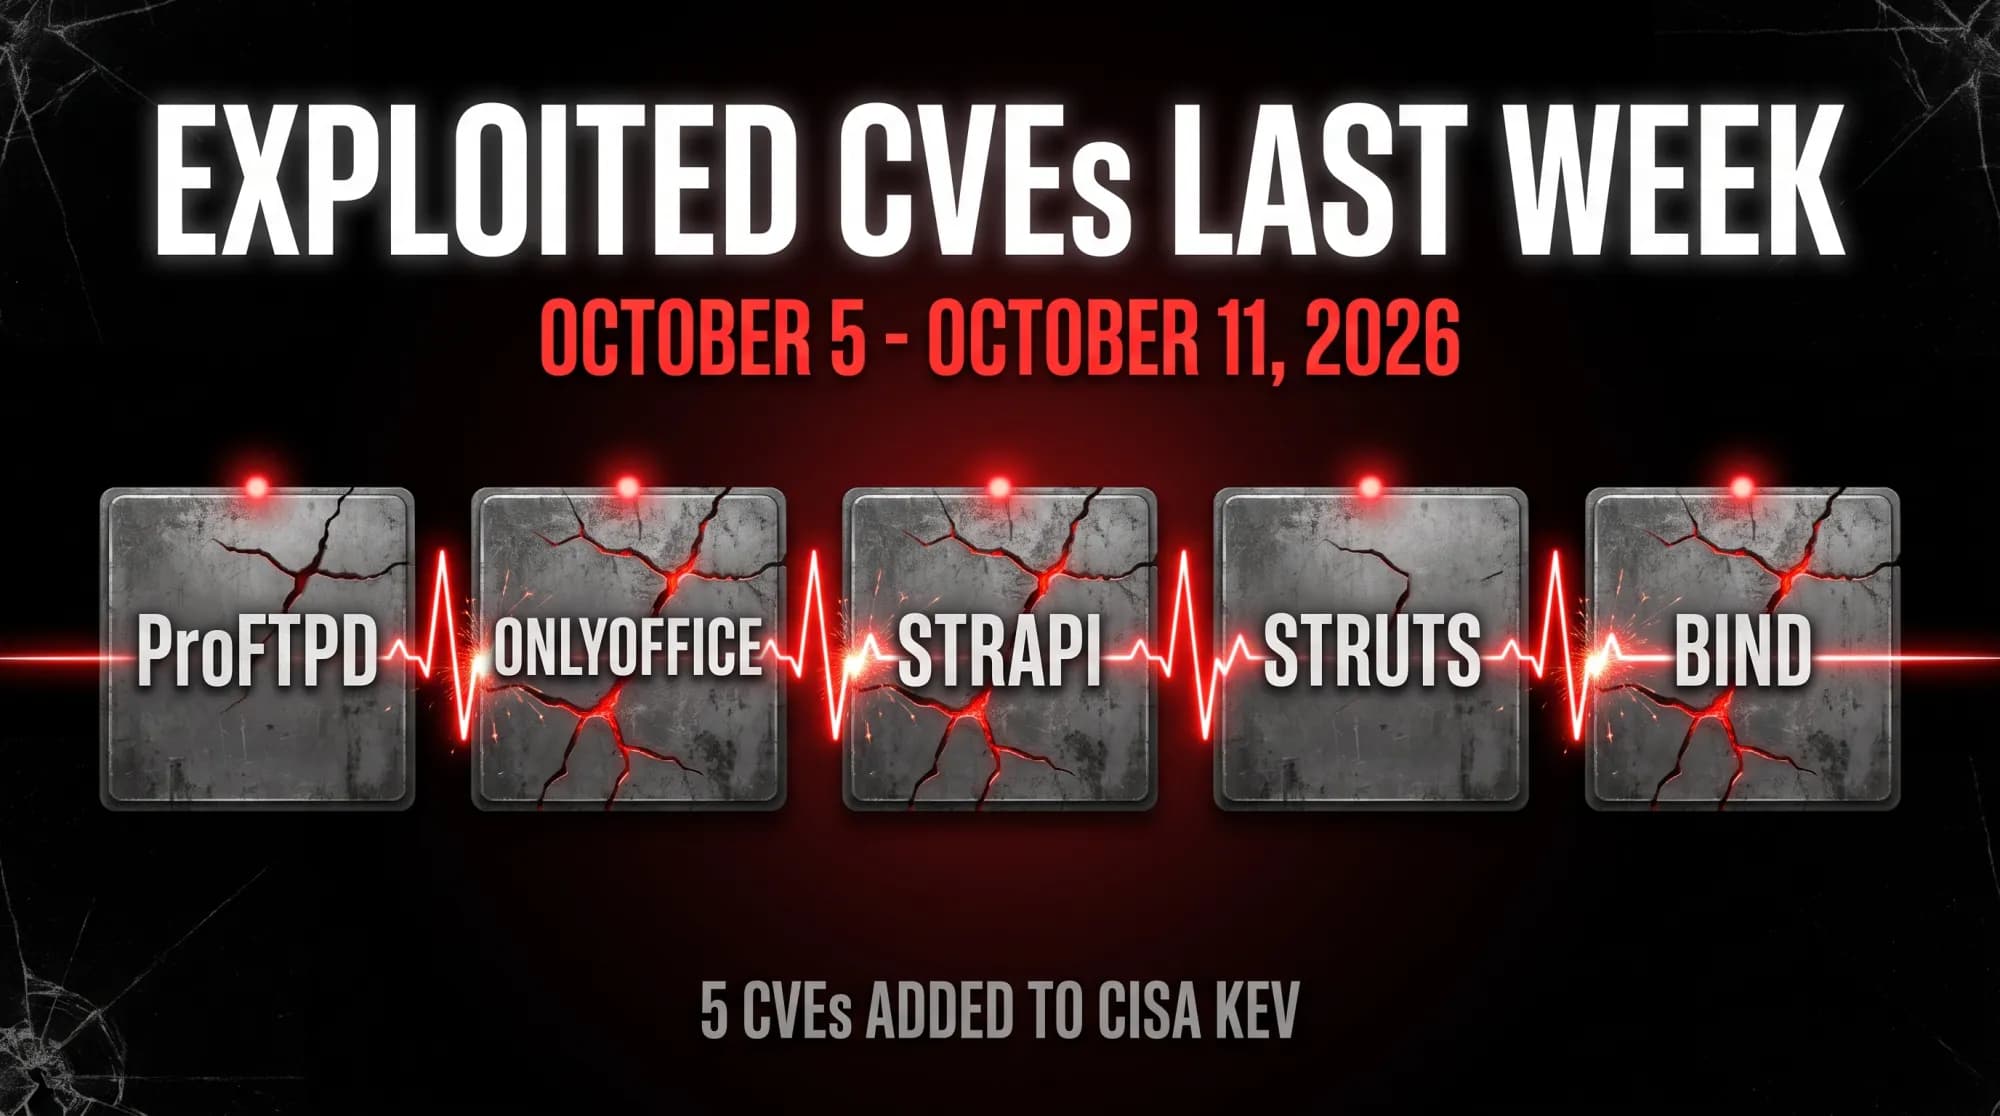
Exploited CVEs Last Week: October 5-11, 2026

CISA added five CVEs to KEV on October 8, all from 2015 to 2023: ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. A joint advisory ties them to a China-linked campaign, and EPSS scores range from 3.6 to 99.5 percent.
5 min read
Exploited CVEs Last Week: September 28-October 4, 2026
Weekly Digest · CISA KEV · Active Exploitation · Apple · Cisco · Citrix · Zammad · Fortinet

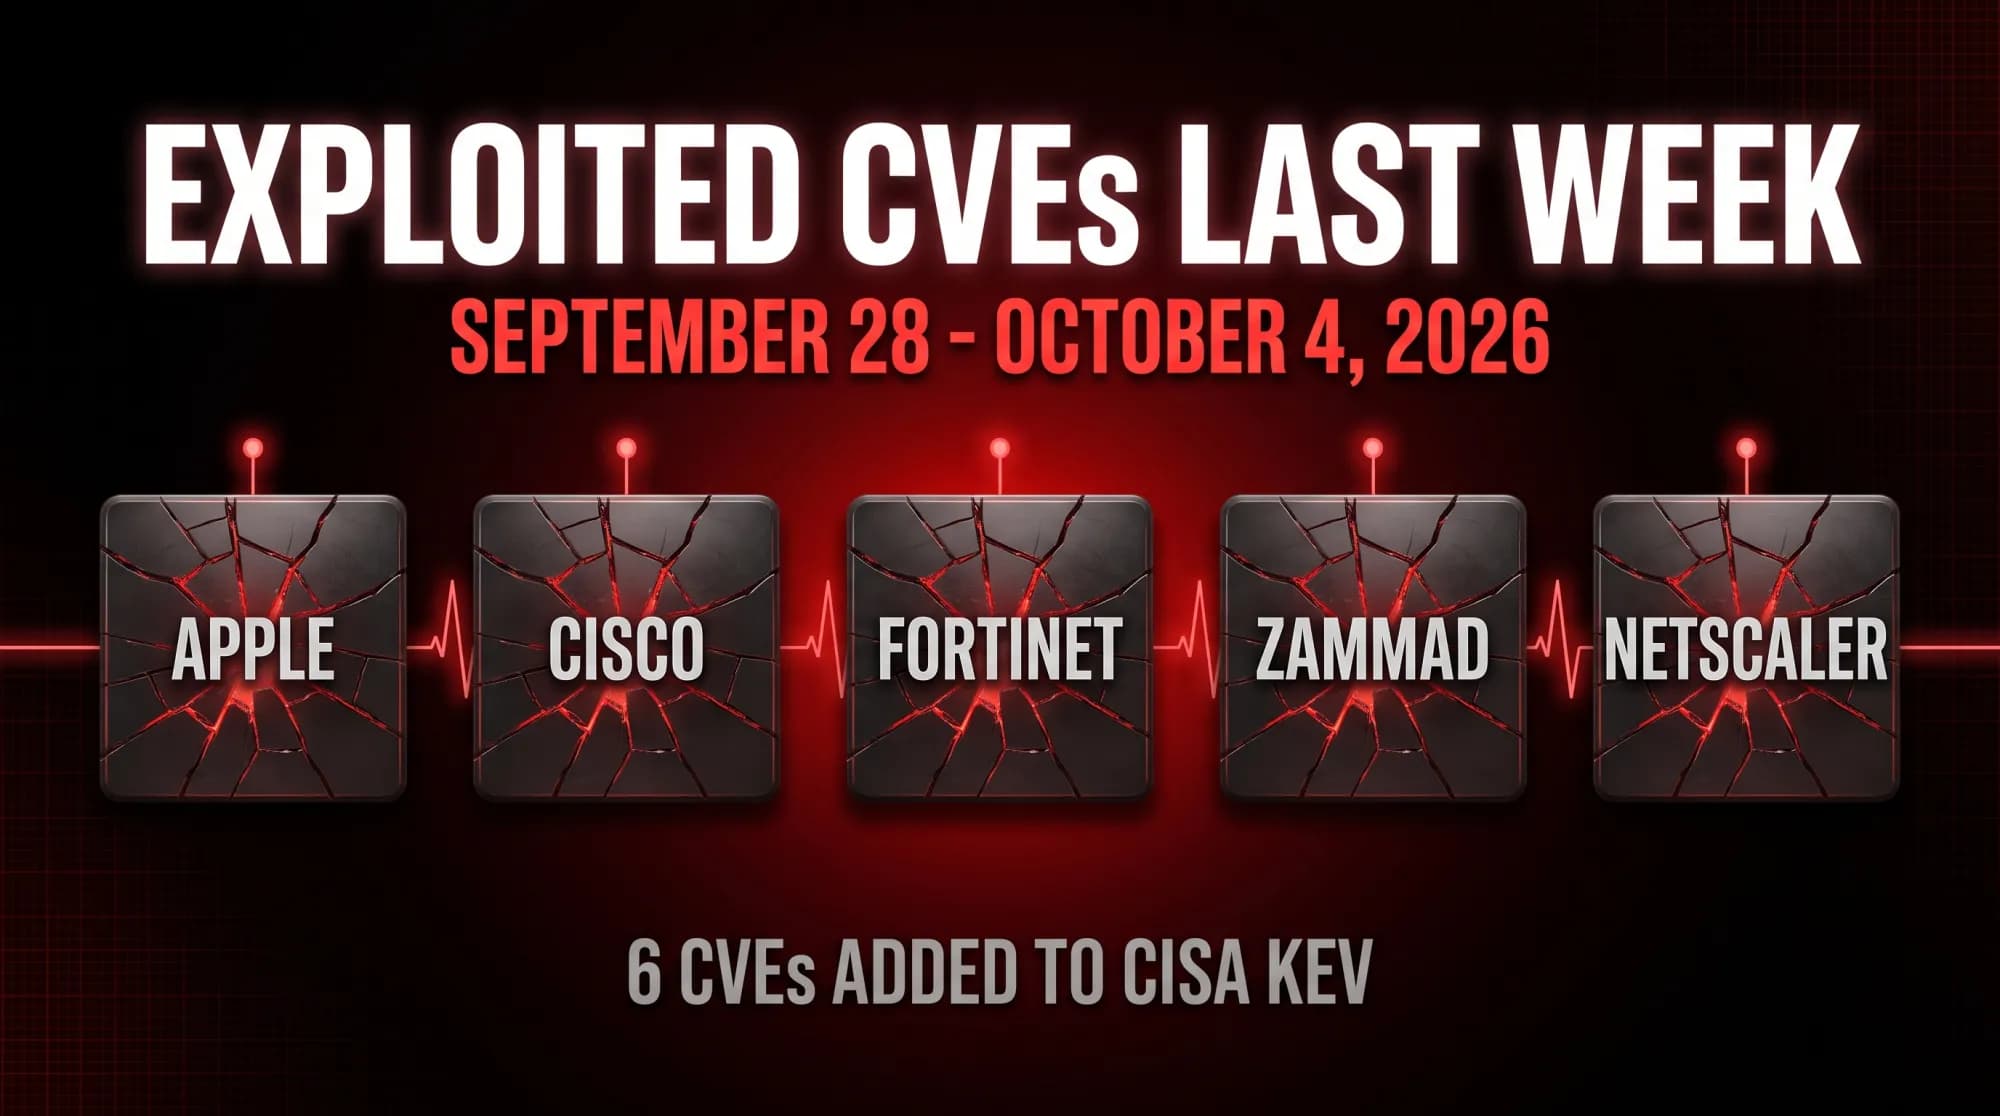
Exploited CVEs Last Week: September 28-October 4, 2026

Six exploited CVEs reached CISA's KEV catalog between September 29 and October 4, covering Apple, Cisco, Fortinet, Zammad, and NetScaler. Each calls for a different first move, from a simple upgrade to a workaround because no patch exists.
4 min read
CVE-2026-88771 & CVE-2026-88772: Citrix NetScaler Zero-Days
Zero-Day · CISA KEV · Active Exploitation · Security Alert · Citrix

CVE-2026-88771 & CVE-2026-88772: Citrix NetScaler Zero-Days

Citrix confirmed active exploitation of two NetScaler zero-days, CVE-2026-88771 and CVE-2026-88772, after a weekend of quiet shutdown warnings and NCSC pre-notifications. Here's the mechanism, who's affected, and the September 30 deadline.

5 min read
Exploited CVEs Last Week: September 21-27, 2026
CISA KEV · Active Exploitation · Weekly Digest · Security Alert

Exploited CVEs Last Week: September 21-27, 2026

CISA added nine actively exploited CVEs to KEV last week, from F5 and Arista to WordPress, SharePoint, MikroTik, and a fresh pair of Citrix NetScaler zero-days. Here's what happened, and what's still due.

6 min read
CVE-2026-5430: WSO2's JWT Algorithm Bypass Is Being Exploited for Lateral Movement
CISA KEV · CVE · Active Exploitation · Security Alert · WSO2

CVE-2026-5430: WSO2's JWT Algorithm Bypass Is Being Exploited for Lateral Movement

WatchTowr's honeypot network caught active exploitation of a WSO2 JWT algorithm bypass, with forged tokens granting full access to every backend API a compromised gateway proxies. CISA added it to KEV; federal agencies must patch by September 27.

4 min read
Critical Next.js ImageResponse RCE (CVE-2026-94545): A 9.5 That Hides in Your Image Generation
RCE · Next.js · Security Alert · Security · Vulnerability · CVE

Critical Next.js ImageResponse RCE (CVE-2026-94545): A 9.5 That Hides in Your Image Generation

Vercel has disclosed a critical remote code execution flaw in the Node.js implementation of ImageResponse in Next.js, tracked as CVE-2026-94545. It carries a CVSS of 9.5, and it is network-reachable with no authentication and no user interaction. But whether it affects you comes down to a detail that a version check alone will not answer: whether untrusted data reaches the SVG your app generates. This is a case where "am I running an affected version" is only half the question. What the vulner

3 min read
CVE-2026-7273: Nearly 1,000 Zyxel Switches Compromised via a Two-Month-Old Patch
Active Exploitation · CISA KEV · Security Alert · Zyxel

CVE-2026-7273: Nearly 1,000 Zyxel Switches Compromised via a Two-Month-Old Patch

CISA confirmed active exploitation of a Zyxel GS1900 switch vulnerability patched back in June, after GreyNoise found nearly 1,000 compromised devices across 48 countries. Here is the mechanism, who is affected, and what is due by September 24.

4 min read
Exploited CVEs Last Week: September 14-21, 2026
Weekly Digest · Active Exploitation · Cisco · Security Alert · Zero-Day · KEV · Linux

Exploited CVEs Last Week: September 14-21, 2026

CISA added seven actively exploited vulnerabilities to its KEV catalog in one week, spanning Cisco, Acronis, Google Pixel, and the Linux kernel. Here is what happened, in order, and what is due today.

6 min read
MikroTik RouterOS Under Active Attack (CVE-2026-86060): When There's No CVSS Score to Wait For
Security Alert · CVE · MikroTik · KEV · Vulnerability · Active Exploitation

MikroTik RouterOS Under Active Attack (CVE-2026-86060): When There's No CVSS Score to Wait For

MikroTik RouterOS is being actively exploited, and CVE-2026-86060 is in the CISA KEV catalog. Here is the interesting part for anyone who prioritizes by severity score: at the time of writing, this CVE has no CVSS score. NVD has not analyzed it yet. If your triage process starts with "what's the CVSS," this one falls through the cracks while attackers are already using it. That gap is exactly what SSVC is built to close. What the vulnerability is CVE-2026-86060 is a privilege escalation flaw

3 min read
Metabase Pre-Auth SQL Injection (CVE-2026-72898): CVSS 10.0, Actively Exploited
Security Alert · CVE · Active Exploitation · Security · Vulnerability

Metabase Pre-Auth SQL Injection (CVE-2026-72898): CVSS 10.0, Actively Exploited

CVE-2026-72898 is an unauthenticated SQL injection in Metabase, scored CVSS 10.0 and already in CISA KEV. One request to /api/session/reset_password gives an attacker admin access and the credentials for every connected database. If you run Metabase, patch today.

2 min read
PostgreSQL to_char Heap Buffer Overflow (CVE-2026-14669): What It Is and How to Read It Fast
Security Alert · CVE · Vulnerability · Security

PostgreSQL to_char Heap Buffer Overflow (CVE-2026-14669): What It Is and How to Read It Fast

CVE-2026-14669 is a CVSS 8.8 HIGH heap buffer overflow in PostgreSQL's to_char function that can run arbitrary code as the database OS user, patched August 13, 2026. Two questions decide your workload: is Postgres in your stack, and is your version older than 18.5 / 17.11 / 16.15 / 15.19 / 14.24?

3 min read
Critical and Already Being Exploited: PAN-OS GlobalProtect Auth Bypass (CVE-2026-0257)
Security Alert · CVE · Active Exploitation · Vulnerability · Security

Critical and Already Being Exploited: PAN-OS GlobalProtect Auth Bypass (CVE-2026-0257)

A 9.1 critical authentication bypass in PAN-OS GlobalProtect, actively exploited and now in CISA KEV. But it only bites under a specific config. The two questions that decide your workload: is the product in your stack, and does your config meet the exposure conditions?

3 min read
Palo Alto Firewall Has an Unpatched Critical RCE Today (CVE-2026-0300)
Security Alert · CVE · Security · Vulnerability

Palo Alto Firewall Has an Unpatched Critical RCE Today (CVE-2026-0300)

Active exploitation of an unauthenticated root RCE in PAN-OS firewalls. No patch until May 13. The one question your team needs to answer in the next two hours: is the User-ID Authentication Portal exposed to the internet?

4 min read
What is a CVE? A Plain-English Guide for Engineering Teams
CVE

What is a CVE? A Plain-English Guide for Engineering Teams

A CVE is a license plate for vulnerabilities. You don't need to memorize acronyms — you need three things: how to tell if a CVE matters to you, what the score means, and what to do when one shows up in your stack.

7 min read
Adobe Reader Zero-Day Exploited for Months Before Emergency Patch
Zero-Day · Active Exploitation · CVE · Vulnerability · Security · Security Alert

Adobe Reader Zero-Day Exploited for Months Before Emergency Patch

CVE-2026-34621 chains two logic bugs to escape Adobe Reader's sandbox — no memory corruption needed. Exploited since December 2025, patched April 11. Russian-language lures targeting oil & gas sector.

3 min read
Palo Alto PAN-OS Vulnerability (CVE-2026-0229) Can Trigger Firewall Reboot Loops
Security Alert · CVE · Vulnerability · Security

Palo Alto PAN-OS Vulnerability (CVE-2026-0229) Can Trigger Firewall Reboot Loops

A denial-of-service vulnerability in PAN-OS Advanced DNS Security (CVE-2026-0229) allows unauthenticated attackers to force firewalls into repeated reboot cycles, potentially pushing them into maintenance mode. Upgrade affected PAN-OS versions immediately.

2 min read
FortiCloud SSO Bypass (CVE-2026-24858): Active Exploitation and What You Need to Know
Security Alert · Active Exploitation · CVE · Vulnerability

FortiCloud SSO Bypass (CVE-2026-24858): Active Exploitation and What You Need to Know

A critical authentication bypass in FortiCloud SSO (CVE-2026-24858, CVSS 9.4) is being actively exploited. Attackers with any FortiCloud account can potentially access devices belonging to other organizations. Patch immediately and audit your admin accounts.

3 min read
Developer Tools

Why You Should Use VulnTracker (If You're a Developer)

Security is important — everyone agrees on that. But for most developers, security tracking is not the job they signed up for. You're building features, fixing bugs, shipping releases...

2 min read