Exploited CVEs Last Week: September 21-27, 2026
CISA added nine actively exploited CVEs to KEV last week, from F5 and Arista to WordPress, SharePoint, MikroTik, and a fresh pair of Citrix NetScaler zero-days. Here's what happened, and what's still due.
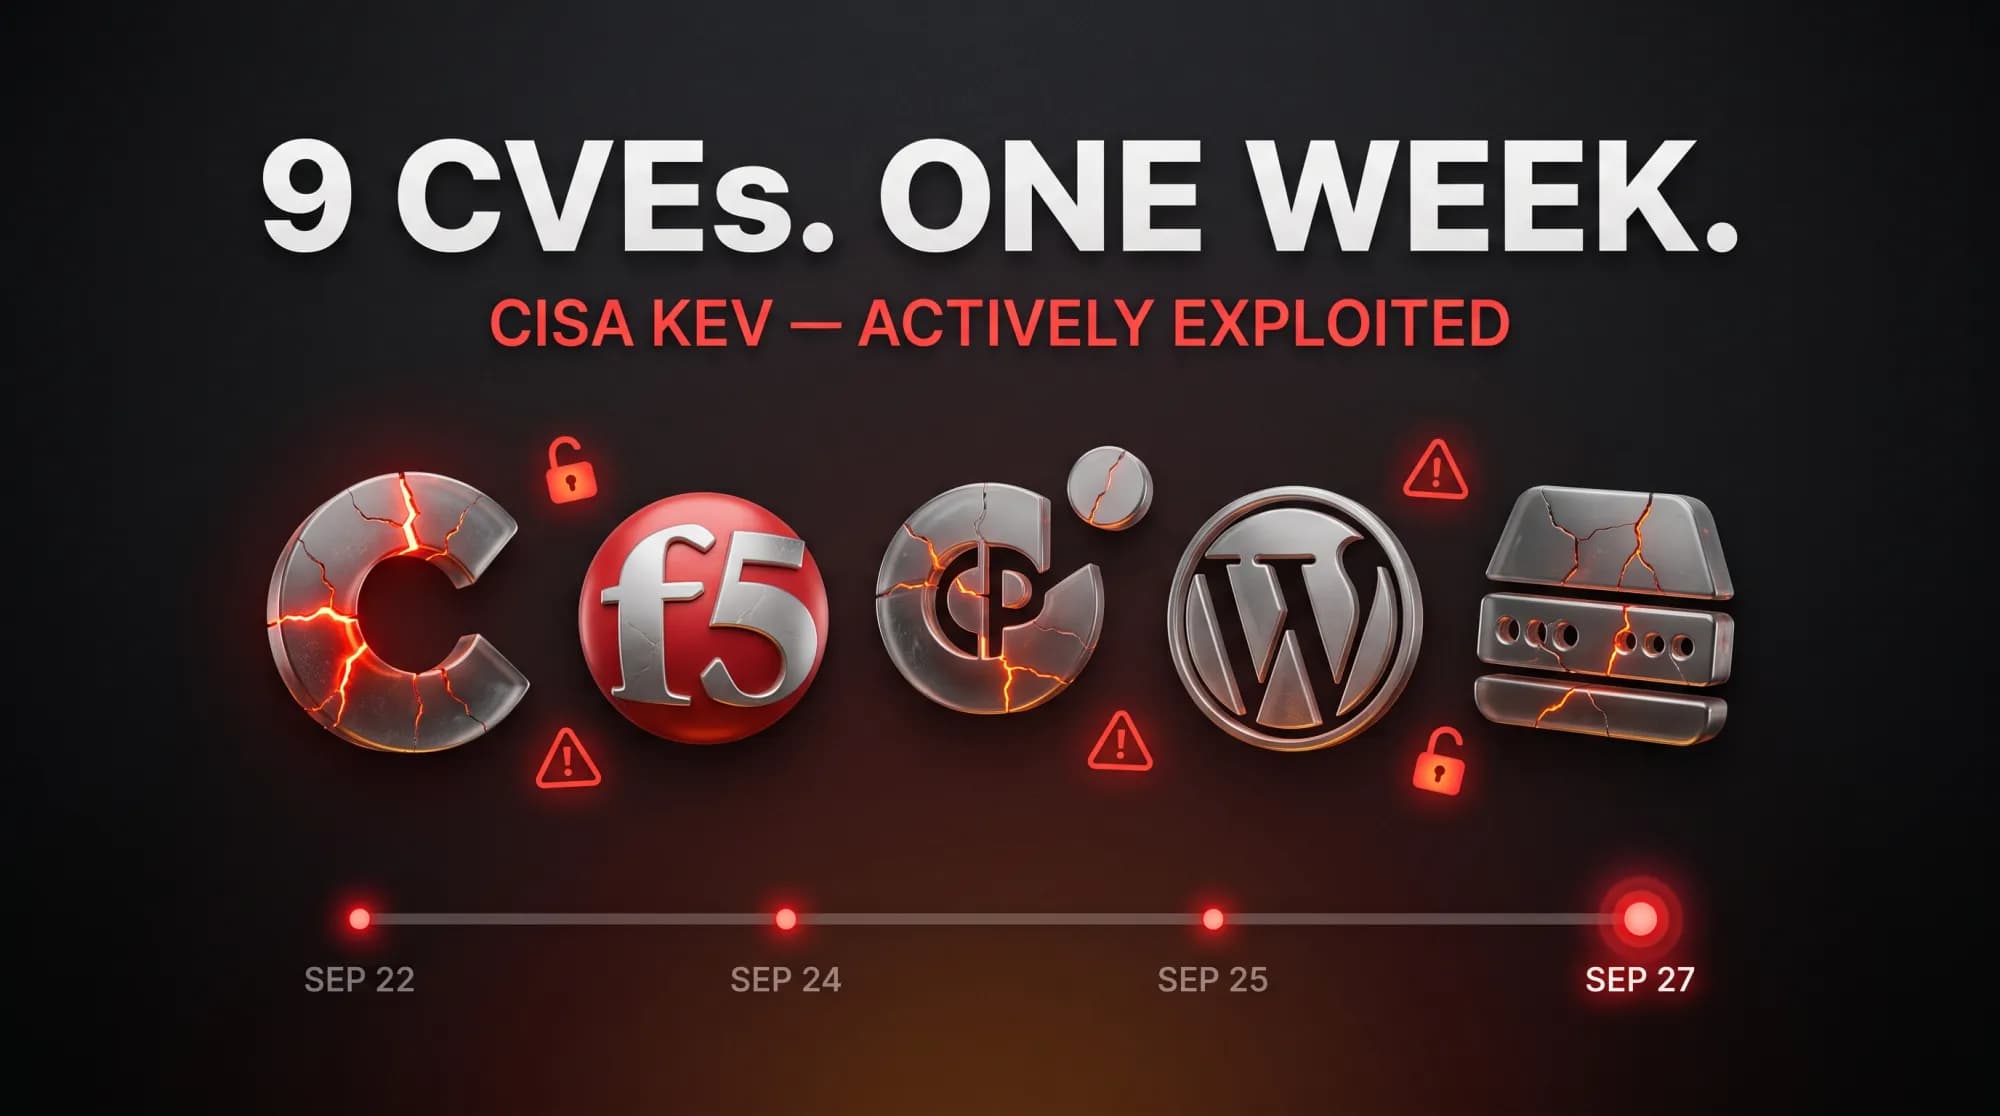
Last week was the busiest stretch CISA's Known Exploited Vulnerabilities catalog has seen in a while. Nine CVEs, four separate additions, spread across September 22, 24, 25, and 27. F5, Arista, and Check Point landed on the same day. Adobe Commerce followed two days later, in the same batch as the WSO2 JWT bypass we already covered separately. Two more days after that, WordPress, Microsoft SharePoint, and MikroTik RouterOS arrived together. And Saturday brought a pair of true zero-days in Citrix NetScaler that are still being actively exploited as this goes out.
Four of these already have federal deadlines that have passed. Two more are due today. One pair has until Tuesday. Here is what happened, in order, and what still needs your attention.
September 22: Three Vendors, One Day
F5 BIG-IP APM (CVE-2026-94127). A heap-based buffer overflow that triggers when a BIG-IP APM access policy and an OAuth profile are both configured on a virtual server acting as an OAuth Authorization Server. The result is unauthenticated remote code execution. CVSS 9.8. F5 found this one internally first, then confirmed it was already being exploited before a patch existed, which makes it a genuine zero-day rather than a bug that sat patched before anyone noticed it.
Arista VeloCloud Orchestrator (CVE-2026-93952). Improper input validation lets an attacker reach unauthorized, privileged functions on the VeloCloud Orchestrator web interface. It requires network access to that interface and the public portion of an Edge authentication certificate, but no valid VCO credentials. CVSS 10.0. Arista's advisory says this one was discovered externally and was already being exploited when reported, not a zero-day in the F5 sense but still live before most defenders knew to look.
Check Point Security Gateway and Spark Firewall (CVE-2026-85102). Improper certificate trust validation during VPN negotiation, CWE-295, allows unauthenticated remote code execution wherever Site-to-Site or Remote Access VPN is enabled. CVSS 9.8. Affects R81.10.x through R82.10; R82.20 is not affected.
All three were added to KEV on September 22 with a three-day deadline. Federal remediation for all three was due September 25. That date has passed.
September 24: Adobe Commerce, and a CVE We Already Covered
Adobe Commerce and Magento Open Source (CVE-2026-71362). An incorrect authorization flaw, CWE-863, across Commerce and Magento Open Source 2.4.4 through 2.4.9, including the B2B branches. CVSS 9.1. What stands out here is the EPSS score: 88 percent, meaning the exploitation prediction model rates this among the most likely CVEs in the entire catalog to see continued exploitation in the next 30 days. Adobe's advisory points to APSB26-92 for the version-to-fix mapping, and an isolated patch is available as an alternative to a full upgrade. Added to KEV September 24, federal deadline September 27. That date has also passed.
CVE-2026-5430, the WSO2 JWT algorithm bypass, was added to KEV the same day in the same batch. We already gave that one its own full writeup, since a forged token there grants access to every backend API a compromised gateway proxies. If you haven't patched WSO2 yet, that is worth reading in full rather than summarized here again.
September 25: A Decade-Old Bug, a SharePoint Flaw, and a Router SSH Bypass
WordPress Core (CVE-2026-87902). The way WordPress resolves page templates lets an unauthenticated attacker make the get_page_template() function include a readable local PHP file from outside the active theme's directories. Combined with the long-known pearcmd.php technique for writing files, this becomes remote code execution. CVSS 9.2. The range of affected versions is what makes this one sting: WordPress Core 4.7.0 through 7.1.1, close to a decade of releases, all without needing any authentication to exploit. Fixed in 7.1.2. Reported by Robert Ressl.
Microsoft SharePoint Server (CVE-2026-65660). Lets an authenticated, low-privileged attacker execute arbitrary code remotely. Affects SharePoint Server 2016, 2019, and Subscription Edition. CVSS 8.8.
MikroTik RouterOS (CVE-2026-67279). An SSH protocol authentication bypass that lets an unauthenticated attacker open a session channel and execute commands, including creating or modifying files on the device. On its own this is scored around 6.5 to 6.9, medium severity, but CERT Polska has confirmed active exploitation since at least September 2, and researchers note it can be chained with CVE-2026-86060 for full administrative access without any credentials at all. Treat the medium CVSS number with caution here; the chain is the real risk.
All three were added to KEV on September 25. SharePoint and MikroTik carry a federal deadline of September 28, which is today. CISA's WordPress alert did not publish a specific federal due date.
September 27: Two True Zero-Days in Citrix NetScaler
CVE-2026-88771 is an improper input validation flaw that enables unauthenticated remote code execution across all affected NetScaler ADC and Gateway deployments, regardless of configuration. CVE-2026-88772 is a memory-overflow vulnerability leading to remote code execution or denial of service, but only when DTLS is enabled, which it is by default on VPN virtual servers. Both carry a CVSS v4 score of 9.5, and unlike most of the entries above, both were actively exploited before Citrix had fixes ready. These are true zero-days, not patched bugs caught in reuse.
Fixed builds are available: 14.1-73.37 for the 14.1 branch, 13.1-64.23 for 13.1, with matching FIPS and NDcPP builds. CISA added both to KEV on September 27 with a federal deadline of September 30.
Reading These on VulnTracker
All nine CVEs are trackable individually, each with the Actively Exploited banner, the CISA KEV Added and Remediation Due dates, and an SSVC panel marking exploitation status, automatability, and impact scope. The automatability flag is worth filtering on this week specifically: several of these, including Arista VeloCloud and Adobe Commerce, are marked Automatable, meaning the exploitation doesn't require manual attacker effort per target, which tends to correlate with faster mass scanning once a working exploit circulates. Use Advanced Search with the Exploited (KEV) and This Week filters to pull up entries like these as they're added, rather than waiting for a roundup like this one.
What to Do Now
- F5 BIG-IP APM, Arista VeloCloud Orchestrator, Check Point Security Gateway, and Adobe Commerce are all past their federal deadlines. If you run any of these and haven't patched, treat it as urgent regardless of what sector you're in.
- Microsoft SharePoint and MikroTik RouterOS are due today. For MikroTik specifically, don't stop at the CVSS number: check whether SSH is exposed to untrusted networks and whether you're also vulnerable to CVE-2026-86060, since the chain matters more than either bug alone.
- Citrix NetScaler has until September 30, but both CVEs were exploited as zero-days, meaning attackers had a head start before any fix existed. If you run NetScaler ADC or Gateway, don't wait for the deadline.
- For WordPress, check your version against the 4.7.0 through 7.1.1 range regardless of how old your install is. Nearly a decade of releases being in scope means plenty of sites are affected that assume they're too old to matter.
- Across all nine, prioritize anything marked Automatable in the SSVC panel first. Automatable exploitation scales faster than exploitation requiring manual attacker effort per target.
The Takeaway
Nine CVEs, four vendors' deadlines already passed, two due today, and a fresh pair of zero-days with three days left on the clock. This is what a normal week looks like now, not an outlier. The difference between organizations that handle a week like this and ones that get caught by it usually isn't headcount. It's whether someone is watching KEV additions as they happen instead of finding out from a roundup like this one, days later.
Add this week's nine CVEs to your watchlist on VulnTracker and get notified the moment any of them changes status, whether that's a new exploitation report, a revised deadline, or a fresh patch.
References
F5 Security Advisory and NVD/CVE.org (CVE-2026-94127); Arista Security Advisory and NVD/CVE.org (CVE-2026-93952); Check Point Security Advisory and NVD/CVE.org (CVE-2026-85102); Adobe Security Bulletin APSB26-92 and NVD/CVE.org (CVE-2026-71362); WordPress Core advisory and NVD/CVE.org (CVE-2026-87902); Microsoft Security Response Center and NVD/CVE.org (CVE-2026-65660); MikroTik advisory, CERT Polska, and NVD/CVE.org (CVE-2026-67279); Citrix Security Bulletin CTX697096 and NVD/CVE.org (CVE-2026-88771, CVE-2026-88772); CISA Known Exploited Vulnerabilities Catalog additions, September 22, 24, 25, and 27, 2026.
Related reading
CVE-2026-88771 & CVE-2026-88772: Citrix NetScaler Zero-Days
Citrix confirmed active exploitation of two NetScaler zero-days, CVE-2026-88771 and CVE-2026-88772, after a weekend of quiet shutdown warnings and NCSC pre-notifications. Here's the mechanism, who's affected, and the September 30 deadline.
CVE-2026-5430: WSO2's JWT Algorithm Bypass Is Being Exploited for Lateral Movement
WatchTowr's honeypot network caught active exploitation of a WSO2 JWT algorithm bypass, with forged tokens granting full access to every backend API a compromised gateway proxies. CISA added it to KEV; federal agencies must patch by September 27.
CVE-2026-7273: Nearly 1,000 Zyxel Switches Compromised via a Two-Month-Old Patch
CISA confirmed active exploitation of a Zyxel GS1900 switch vulnerability patched back in June, after GreyNoise found nearly 1,000 compromised devices across 48 countries. Here is the mechanism, who is affected, and what is due by September 24.