Topic

Active Exploitation

Latest Active Exploitation coverage — 35 articles.

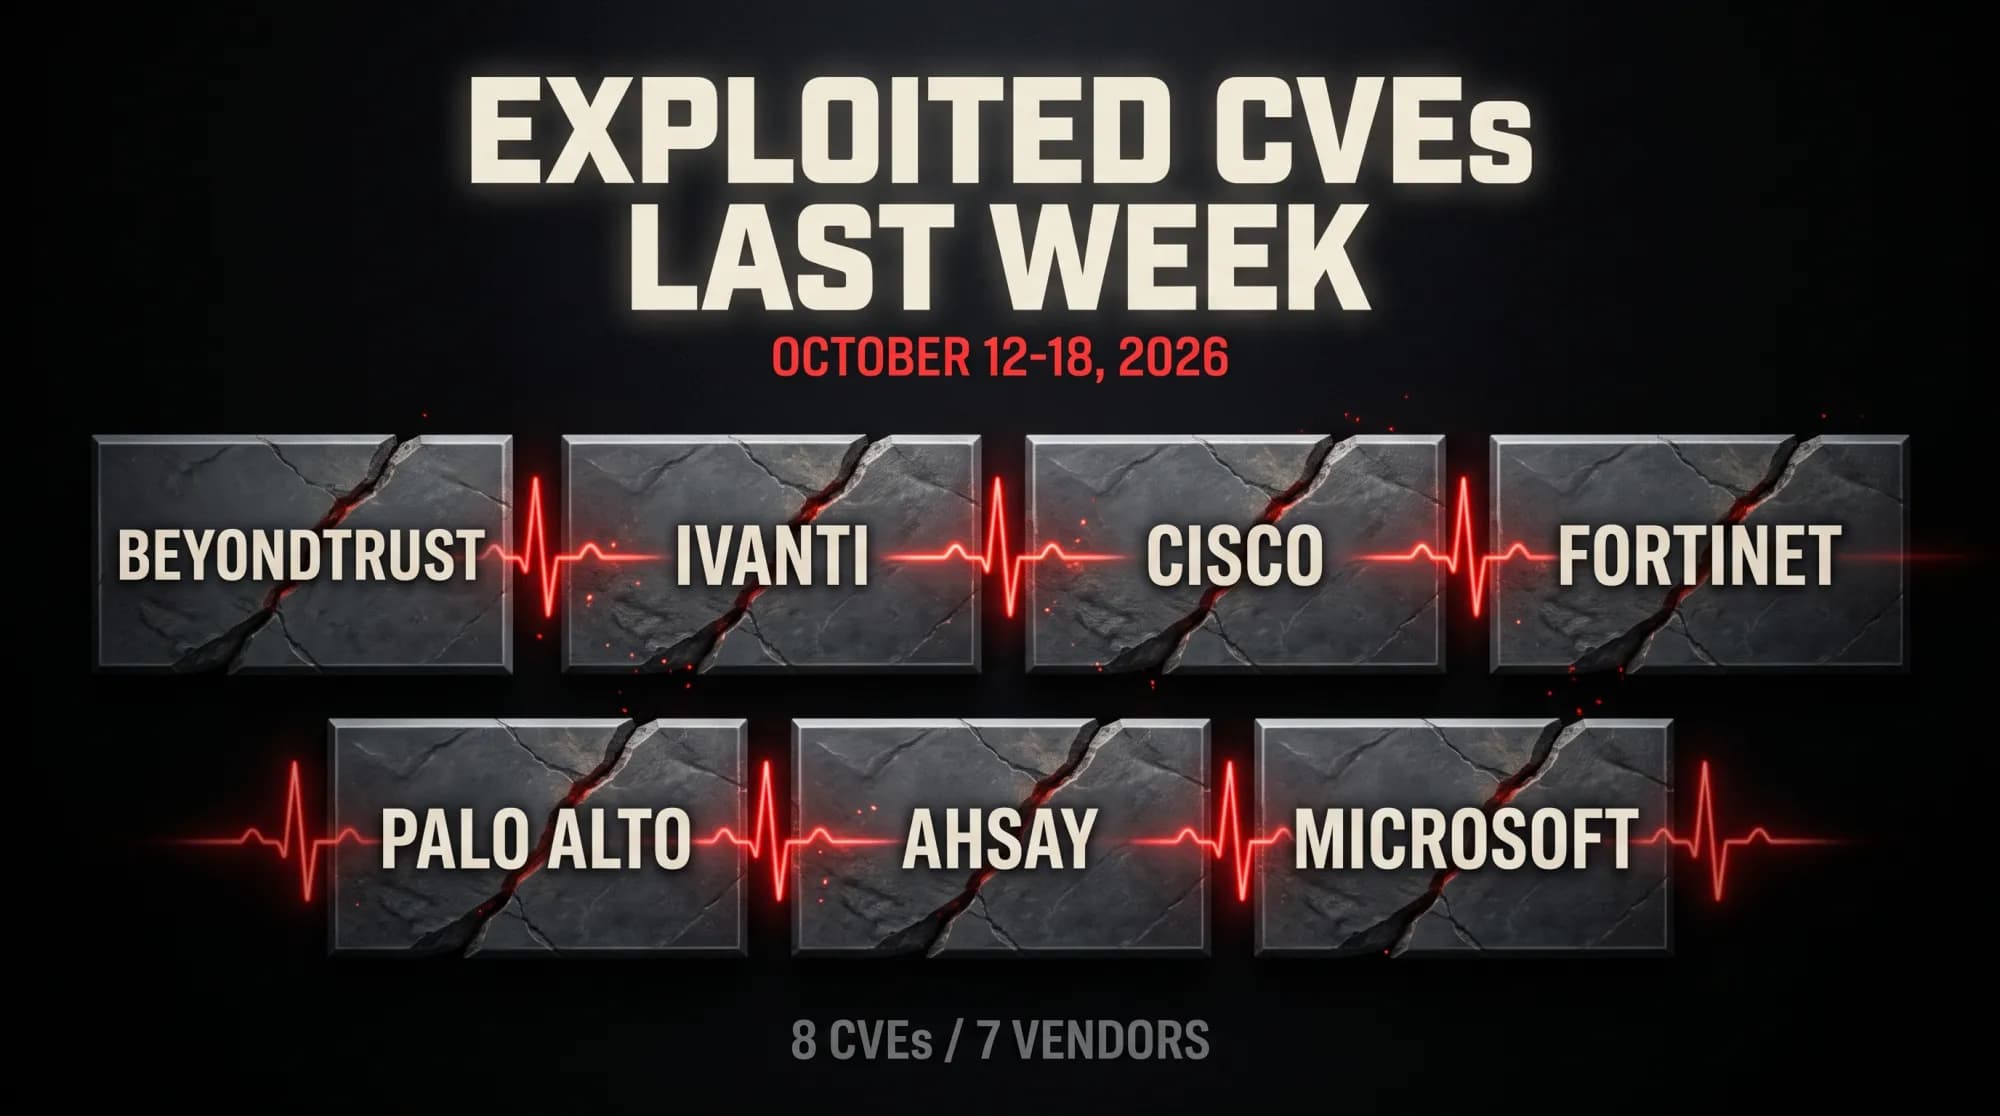
Exploited CVEs Last Week: October 12-18, 2026
Weekly Digest · Active Exploitation · CISA KEV

Exploited CVEs Last Week: October 12-18, 2026

Eight exploited CVEs from seven vendors entered CISA's KEV catalog between October 13 and 16. Five sit on edge or remote access products, seven had an EPSS of 5% or less, and all are marked Active in SSVC. Here is the list, the angle and what to patch first.

6 min read
CVE-2025-61624: PEERSTITCH Malware Abuses a FortiOS Path Traversal Flaw
Fortinet · CISA KEV · Active Exploitation · FortiOS · Malware

CVE-2025-61624: PEERSTITCH Malware Abuses a FortiOS Path Traversal Flaw

Fortinet fixed CVE-2025-61624 in April and rated it Medium. In October, CISA added it to KEV after Unit 42 showed it helping deploy PEERSTITCH, a memory-only implant on FortiGate firewalls. Here are the fixed versions and what to hunt for.

7 min read
Exploited CVEs Last Week: October 5-11, 2026
Active Exploitation · CISA KEV · Weekly Digest

Exploited CVEs Last Week: October 5-11, 2026

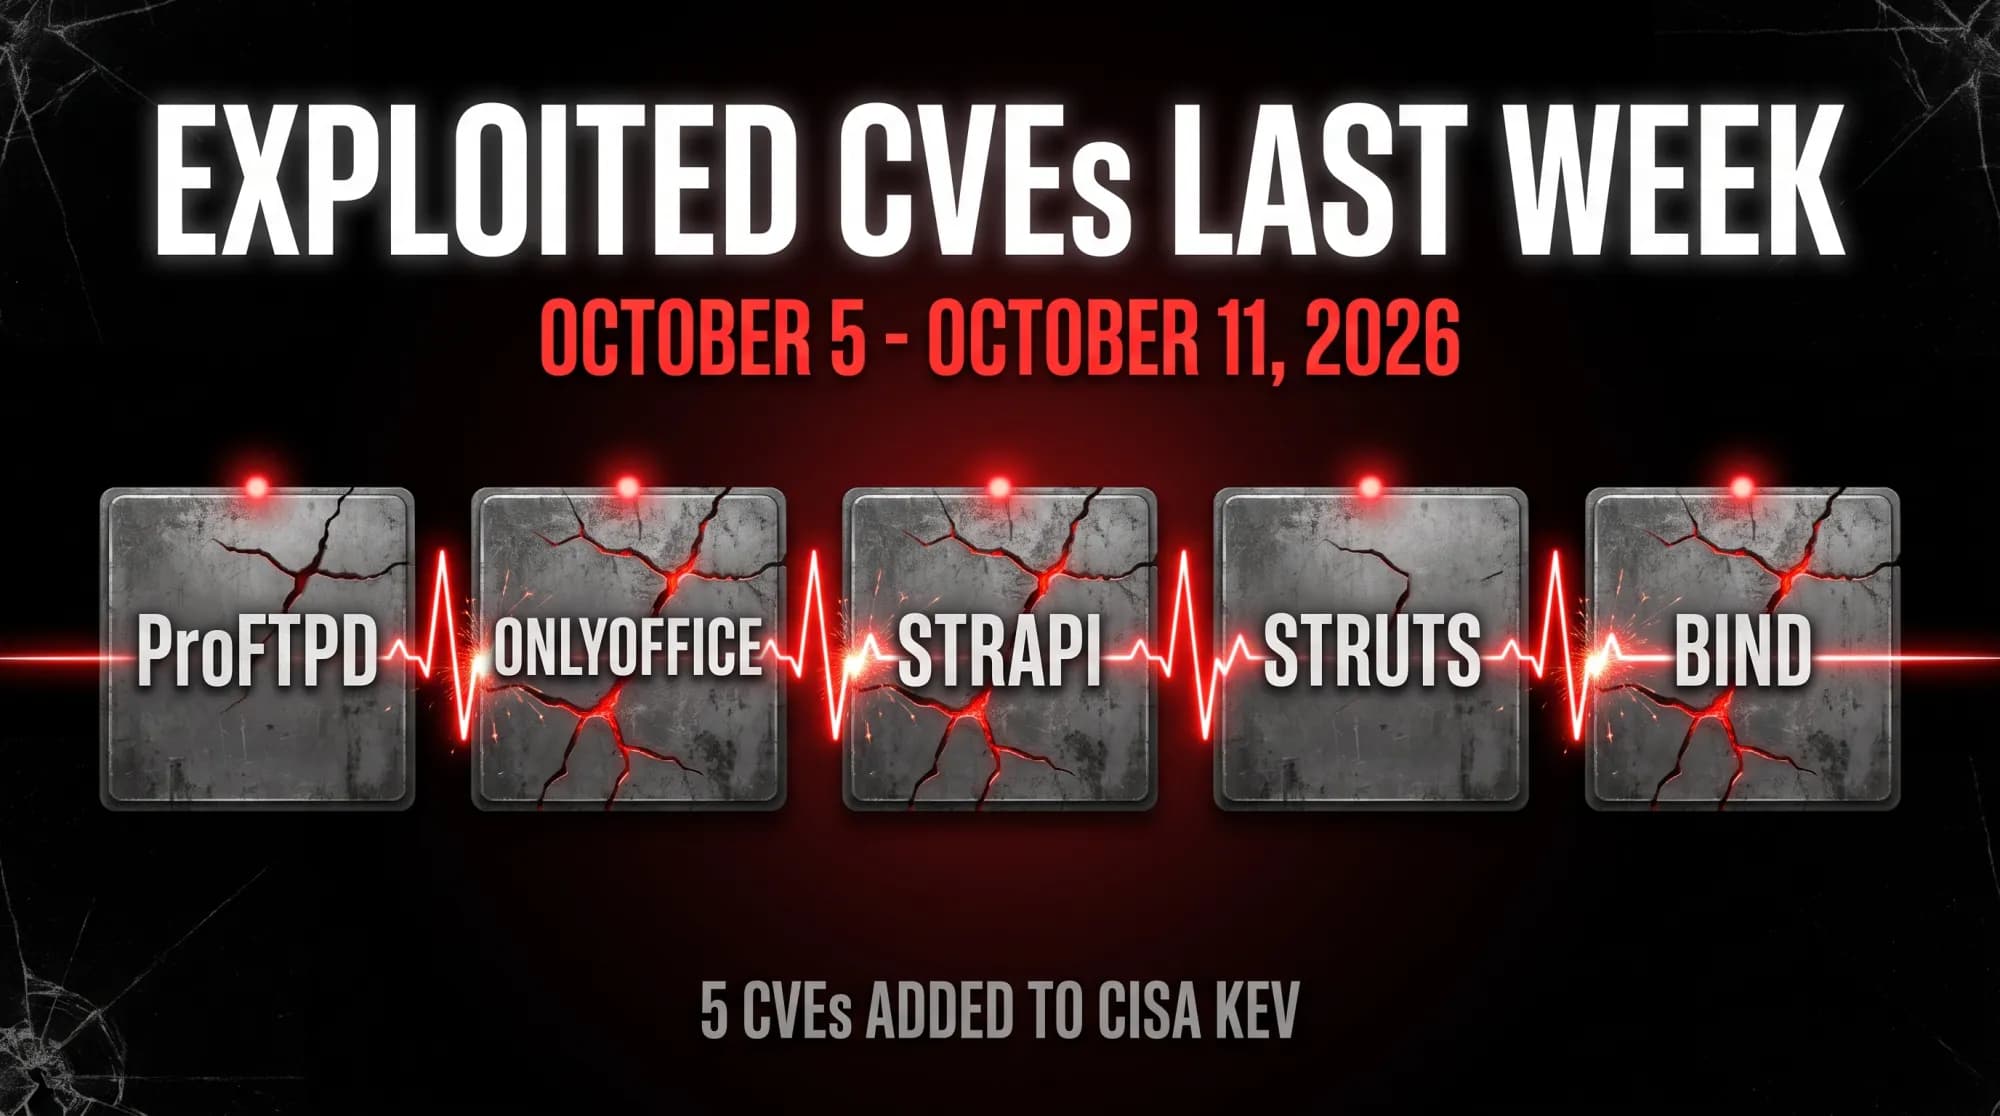
CISA added five CVEs to KEV on October 8, all from 2015 to 2023: ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. A joint advisory ties them to a China-linked campaign, and EPSS scores range from 3.6 to 99.5 percent.

5 min read
Exploited CVEs Last Week: September 28-October 4, 2026
Weekly Digest · CISA KEV · Active Exploitation · Apple · Cisco · Citrix · Zammad · Fortinet

Exploited CVEs Last Week: September 28-October 4, 2026

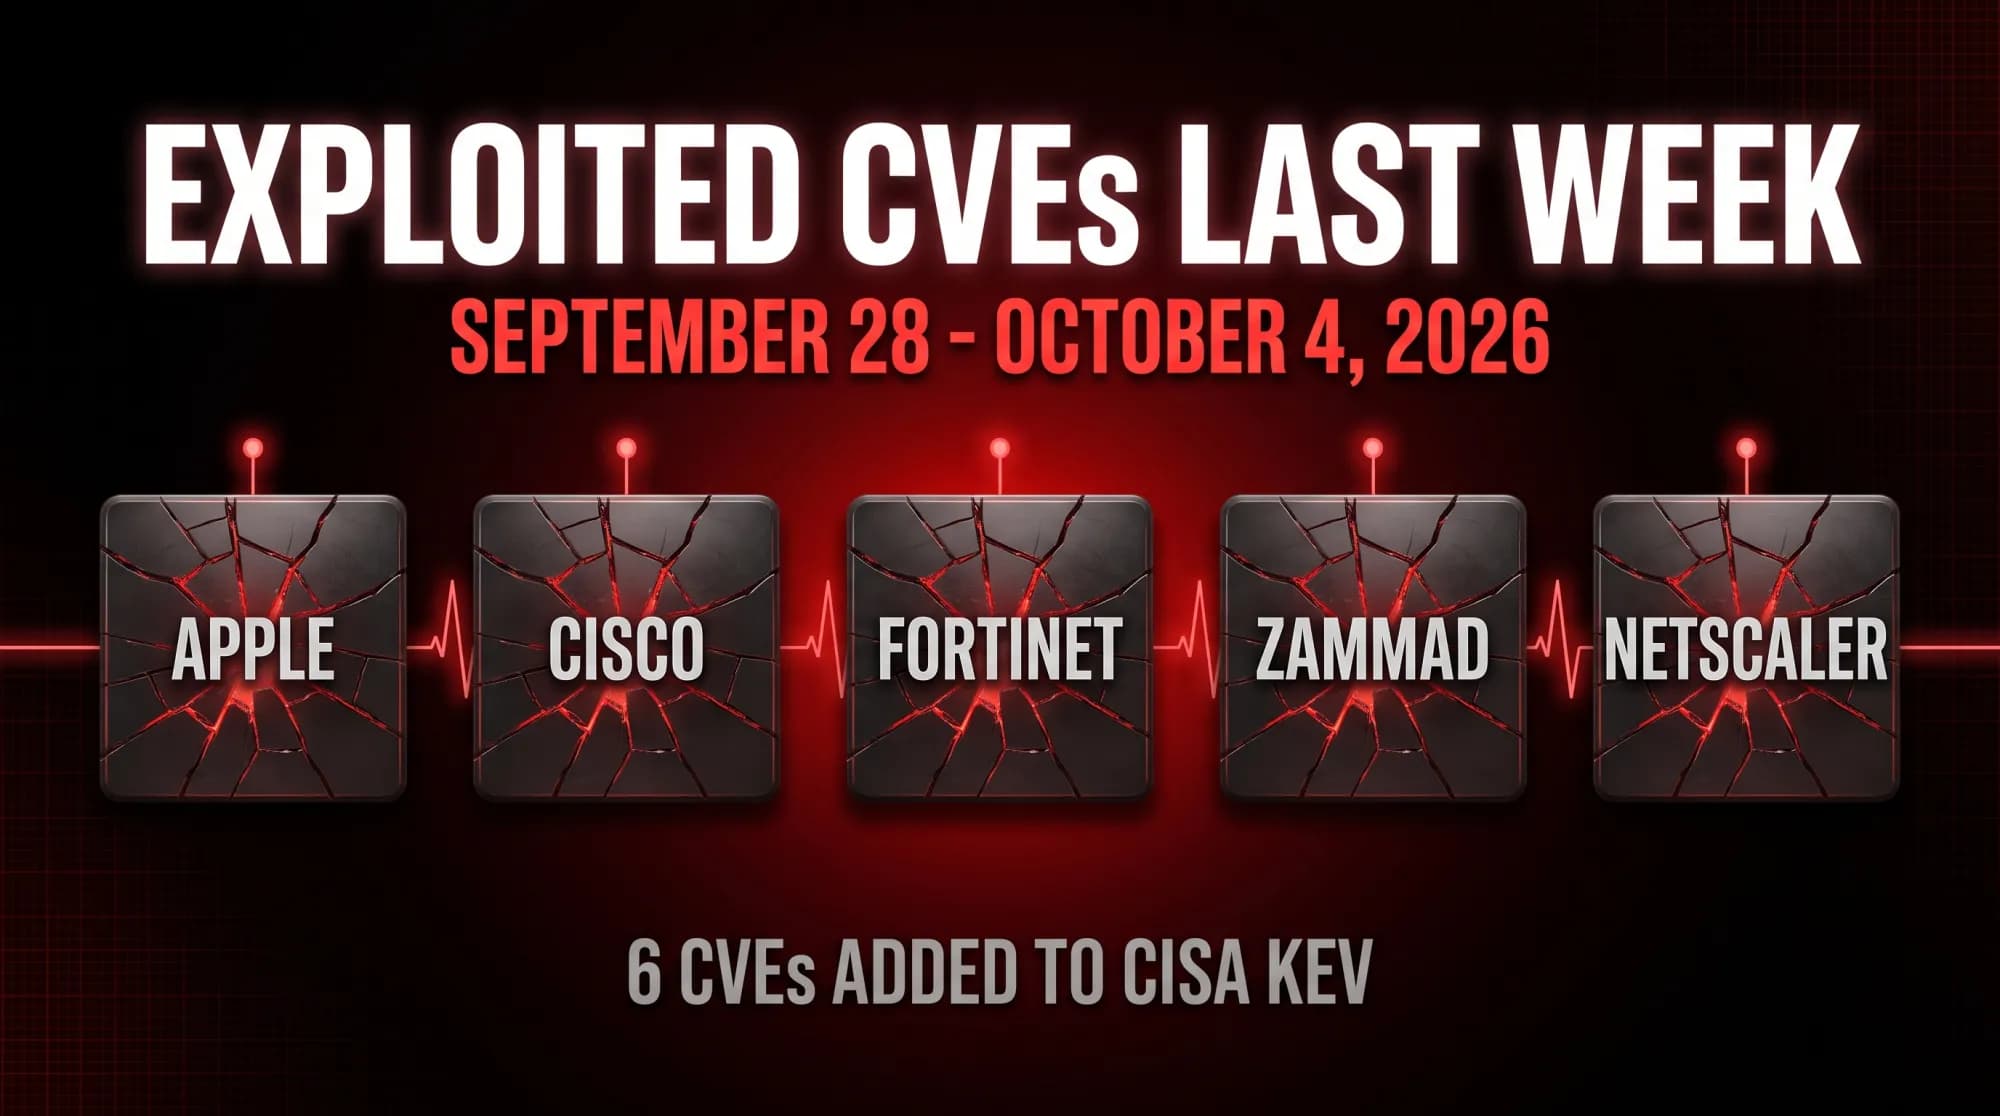
Six exploited CVEs reached CISA's KEV catalog between September 29 and October 4, covering Apple, Cisco, Fortinet, Zammad, and NetScaler. Each calls for a different first move, from a simple upgrade to a workaround because no patch exists.

4 min read
CVE-2026-88771 & CVE-2026-88772: Citrix NetScaler Zero-Days
Zero-Day · CISA KEV · Active Exploitation · Security Alert · Citrix

CVE-2026-88771 & CVE-2026-88772: Citrix NetScaler Zero-Days

Citrix confirmed active exploitation of two NetScaler zero-days, CVE-2026-88771 and CVE-2026-88772, after a weekend of quiet shutdown warnings and NCSC pre-notifications. Here's the mechanism, who's affected, and the September 30 deadline.

5 min read
Exploited CVEs Last Week: September 21-27, 2026
CISA KEV · Active Exploitation · Weekly Digest · Security Alert

Exploited CVEs Last Week: September 21-27, 2026

CISA added nine actively exploited CVEs to KEV last week, from F5 and Arista to WordPress, SharePoint, MikroTik, and a fresh pair of Citrix NetScaler zero-days. Here's what happened, and what's still due.

6 min read
CVE-2026-5430: WSO2's JWT Algorithm Bypass Is Being Exploited for Lateral Movement
CISA KEV · CVE · Active Exploitation · Security Alert · WSO2

CVE-2026-5430: WSO2's JWT Algorithm Bypass Is Being Exploited for Lateral Movement

WatchTowr's honeypot network caught active exploitation of a WSO2 JWT algorithm bypass, with forged tokens granting full access to every backend API a compromised gateway proxies. CISA added it to KEV; federal agencies must patch by September 27.

4 min read
CVE-2026-7273: Nearly 1,000 Zyxel Switches Compromised via a Two-Month-Old Patch
Active Exploitation · CISA KEV · Security Alert · Zyxel

CVE-2026-7273: Nearly 1,000 Zyxel Switches Compromised via a Two-Month-Old Patch

CISA confirmed active exploitation of a Zyxel GS1900 switch vulnerability patched back in June, after GreyNoise found nearly 1,000 compromised devices across 48 countries. Here is the mechanism, who is affected, and what is due by September 24.

4 min read
Exploited CVEs Last Week: September 14-21, 2026
Weekly Digest · Active Exploitation · Cisco · Security Alert · Zero-Day · KEV · Linux

Exploited CVEs Last Week: September 14-21, 2026

CISA added seven actively exploited vulnerabilities to its KEV catalog in one week, spanning Cisco, Acronis, Google Pixel, and the Linux kernel. Here is what happened, in order, and what is due today.

6 min read
MikroTik RouterOS Under Active Attack (CVE-2026-86060): When There's No CVSS Score to Wait For
Security Alert · CVE · MikroTik · KEV · Vulnerability · Active Exploitation

MikroTik RouterOS Under Active Attack (CVE-2026-86060): When There's No CVSS Score to Wait For

MikroTik RouterOS is being actively exploited, and CVE-2026-86060 is in the CISA KEV catalog. Here is the interesting part for anyone who prioritizes by severity score: at the time of writing, this CVE has no CVSS score. NVD has not analyzed it yet. If your triage process starts with "what's the CVSS," this one falls through the cracks while attackers are already using it. That gap is exactly what SSVC is built to close. What the vulnerability is CVE-2026-86060 is a privilege escalation flaw

3 min read
Metabase Pre-Auth SQL Injection (CVE-2026-72898): CVSS 10.0, Actively Exploited
Security Alert · CVE · Active Exploitation · Security · Vulnerability

Metabase Pre-Auth SQL Injection (CVE-2026-72898): CVSS 10.0, Actively Exploited

CVE-2026-72898 is an unauthenticated SQL injection in Metabase, scored CVSS 10.0 and already in CISA KEV. One request to /api/session/reset_password gives an attacker admin access and the credentials for every connected database. If you run Metabase, patch today.

2 min read
Critical and Already Being Exploited: PAN-OS GlobalProtect Auth Bypass (CVE-2026-0257)
Security Alert · CVE · Active Exploitation · Vulnerability · Security

Critical and Already Being Exploited: PAN-OS GlobalProtect Auth Bypass (CVE-2026-0257)

A 9.1 critical authentication bypass in PAN-OS GlobalProtect, actively exploited and now in CISA KEV. But it only bites under a specific config. The two questions that decide your workload: is the product in your stack, and does your config meet the exposure conditions?

3 min read
Adobe Reader Zero-Day Exploited for Months Before Emergency Patch
Zero-Day · Active Exploitation · CVE · Vulnerability · Security · Security Alert

Adobe Reader Zero-Day Exploited for Months Before Emergency Patch

CVE-2026-34621 chains two logic bugs to escape Adobe Reader's sandbox — no memory corruption needed. Exploited since December 2025, patched April 11. Russian-language lures targeting oil & gas sector.

3 min read
FortiCloud SSO Bypass (CVE-2026-24858): Active Exploitation and What You Need to Know
Security Alert · Active Exploitation · CVE · Vulnerability

FortiCloud SSO Bypass (CVE-2026-24858): Active Exploitation and What You Need to Know

A critical authentication bypass in FortiCloud SSO (CVE-2026-24858, CVSS 9.4) is being actively exploited. Attackers with any FortiCloud account can potentially access devices belonging to other organizations. Patch immediately and audit your admin accounts.

3 min read