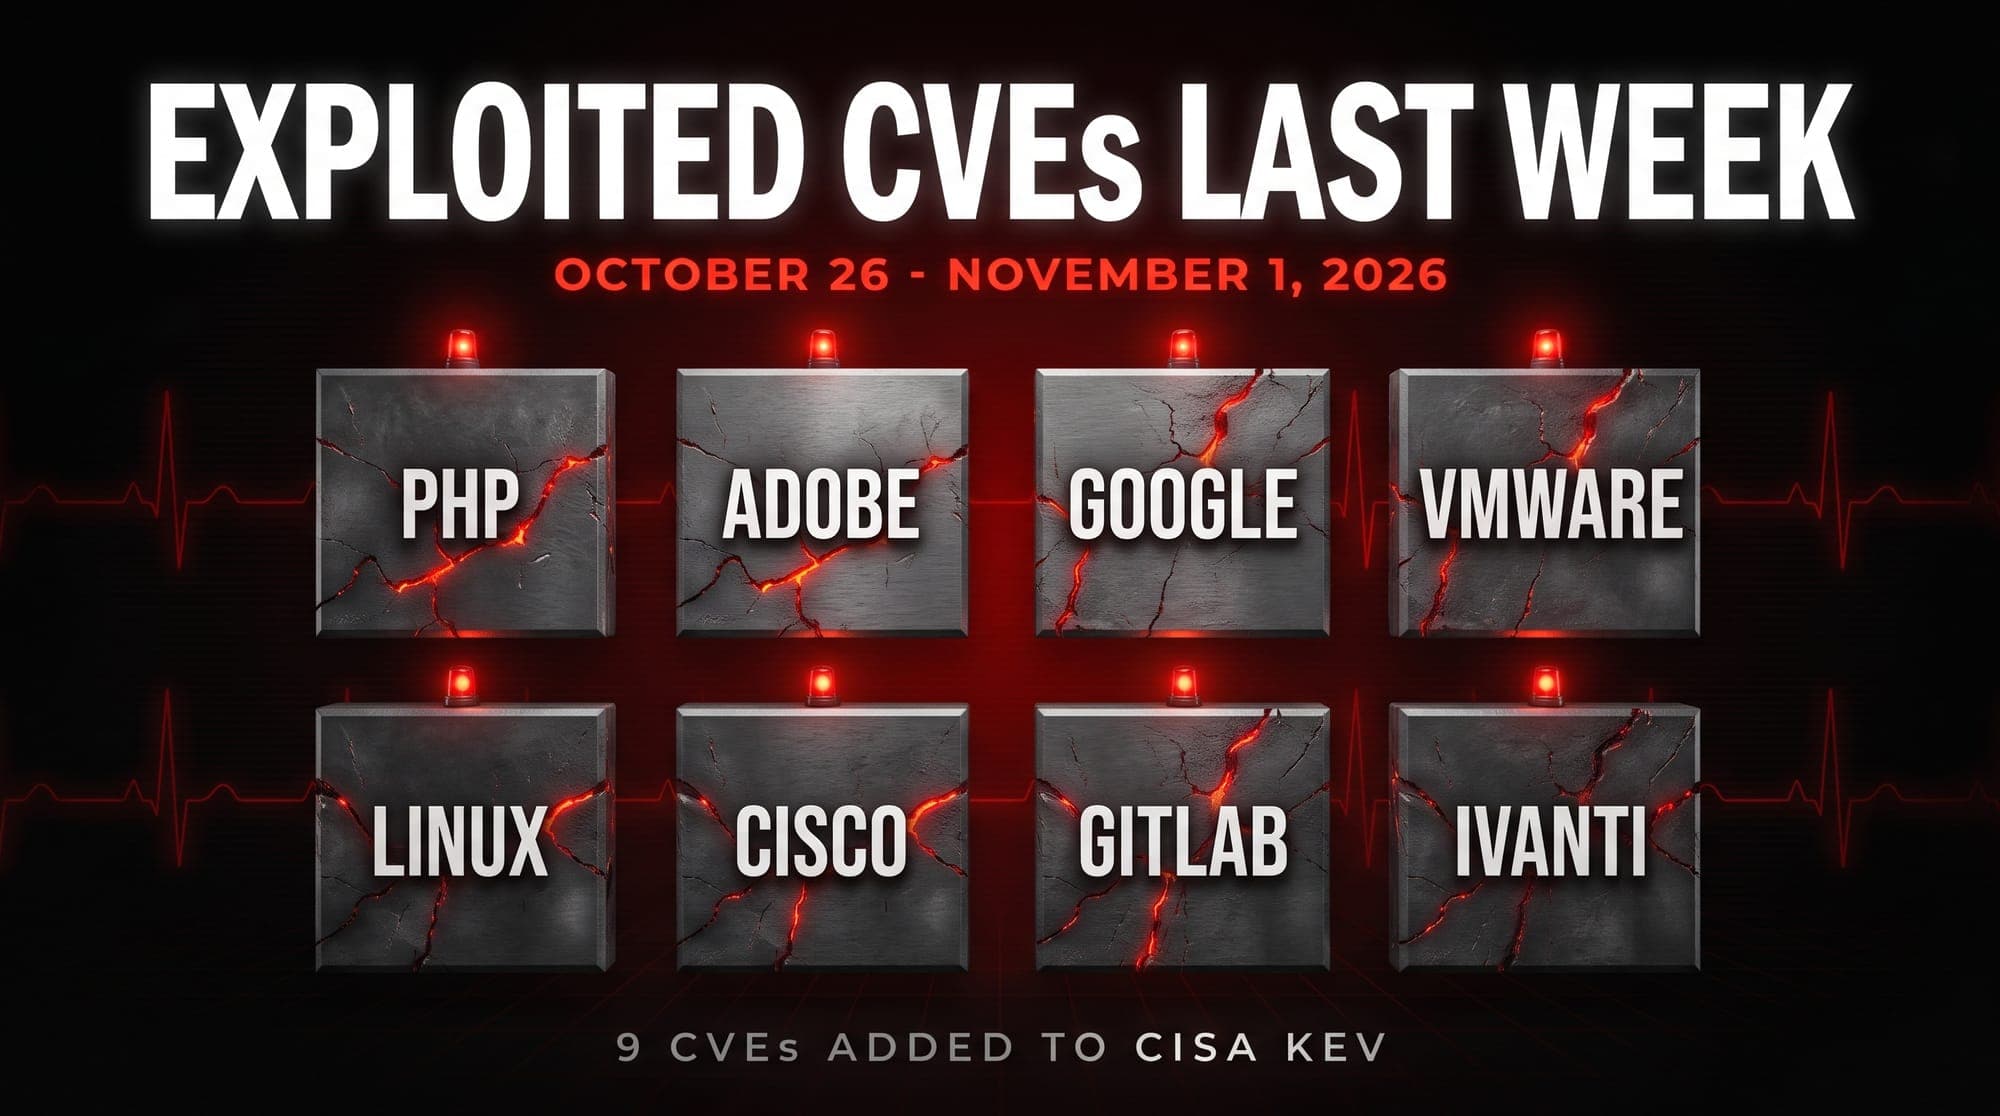
Exploited CVEs Oct 26-Nov 1, 2026
Nine CVEs from eight vendors joined CISA KEV last week, from a 2.7 VMware logging flaw to a CVSS 10.0 GitLab bug. Same SSVC tags got three-day and 14-day deadlines, so here is what to patch first and why.
Topic
Latest Weekly Digest coverage — 7 articles.
Nine CVEs from eight vendors joined CISA KEV last week, from a 2.7 VMware logging flaw to a CVSS 10.0 GitLab bug. Same SSVC tags got three-day and 14-day deadlines, so here is what to patch first and why.
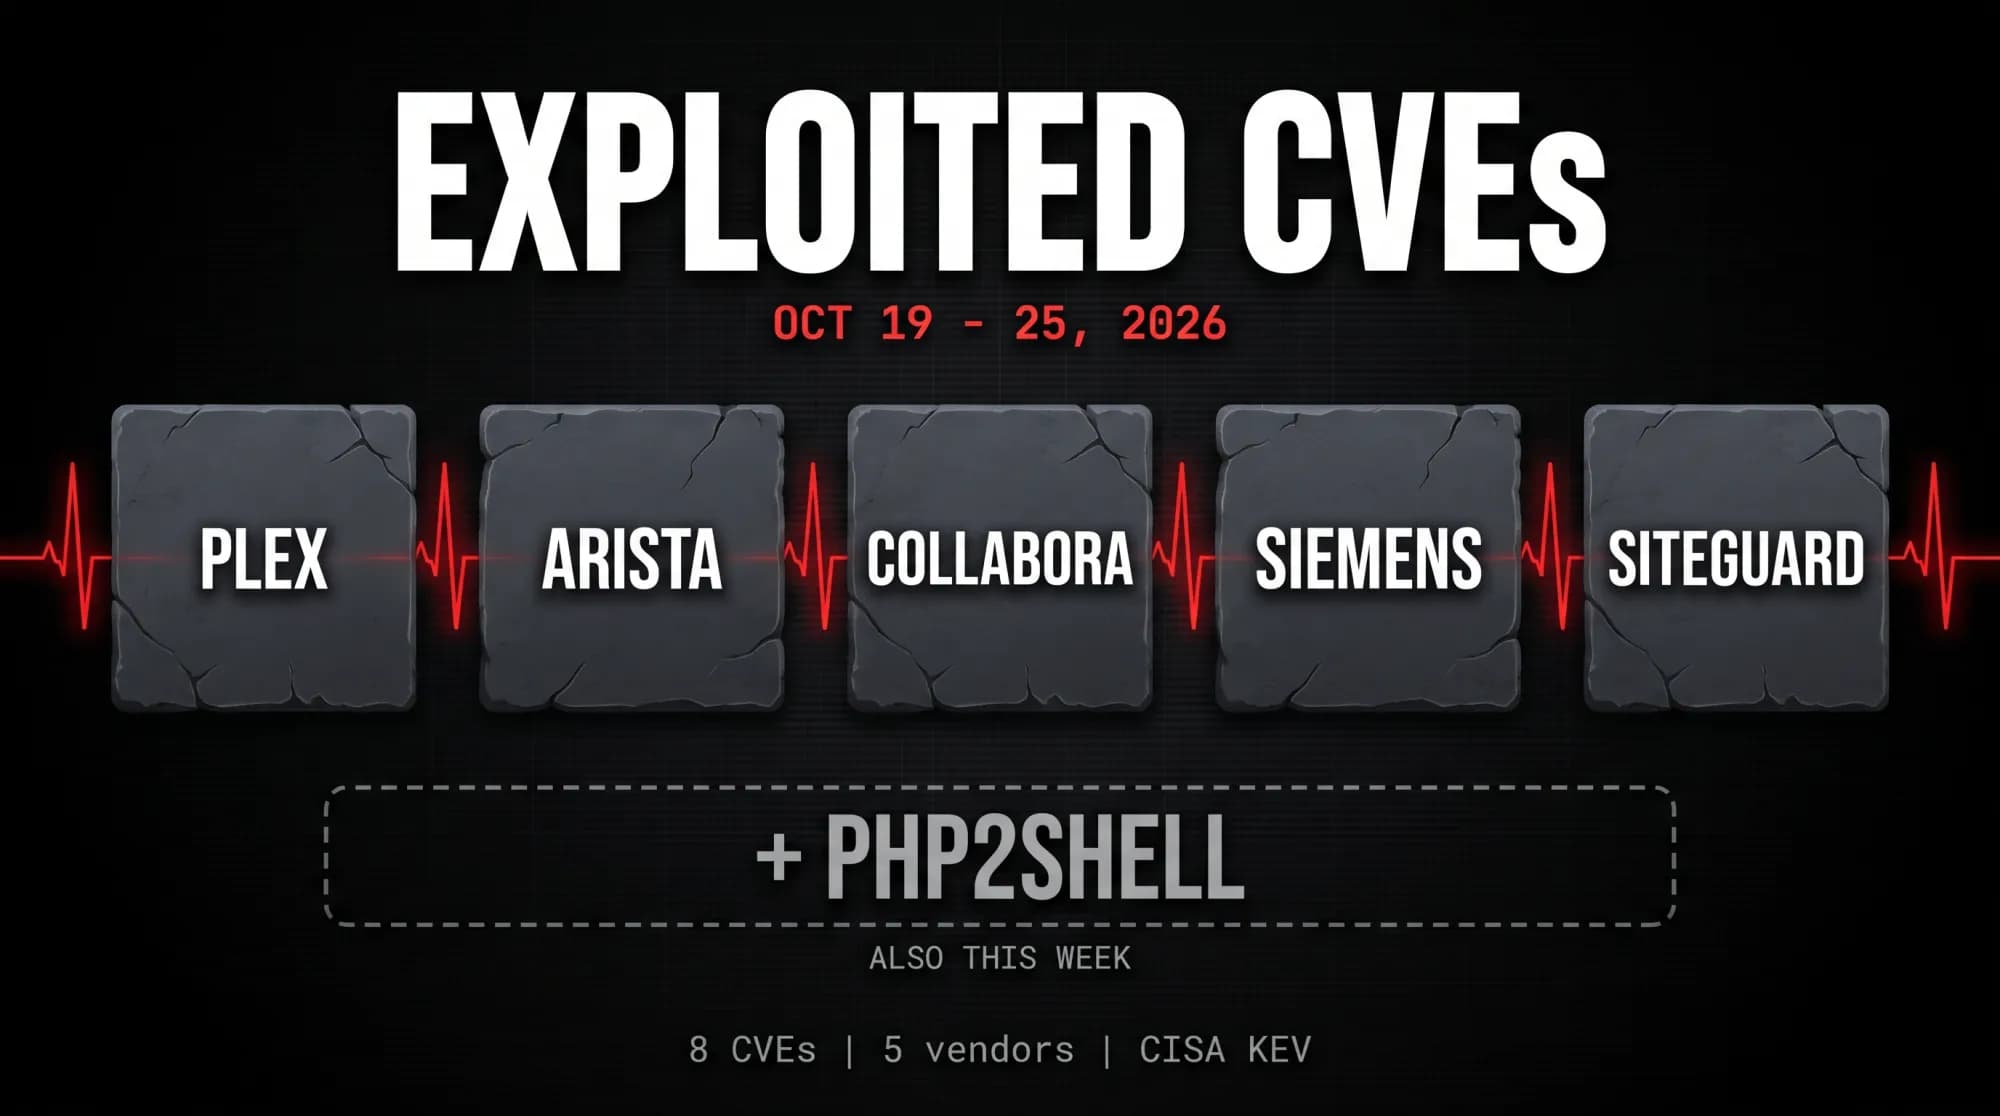
Eight CVEs from five vendors joined CISA KEV this week, with scores from 4.3 to 9.9. Plex2Shell, Siemens ClickFix, SiteGuard, Arista and Collabora, plus where PHP2Shell fits.
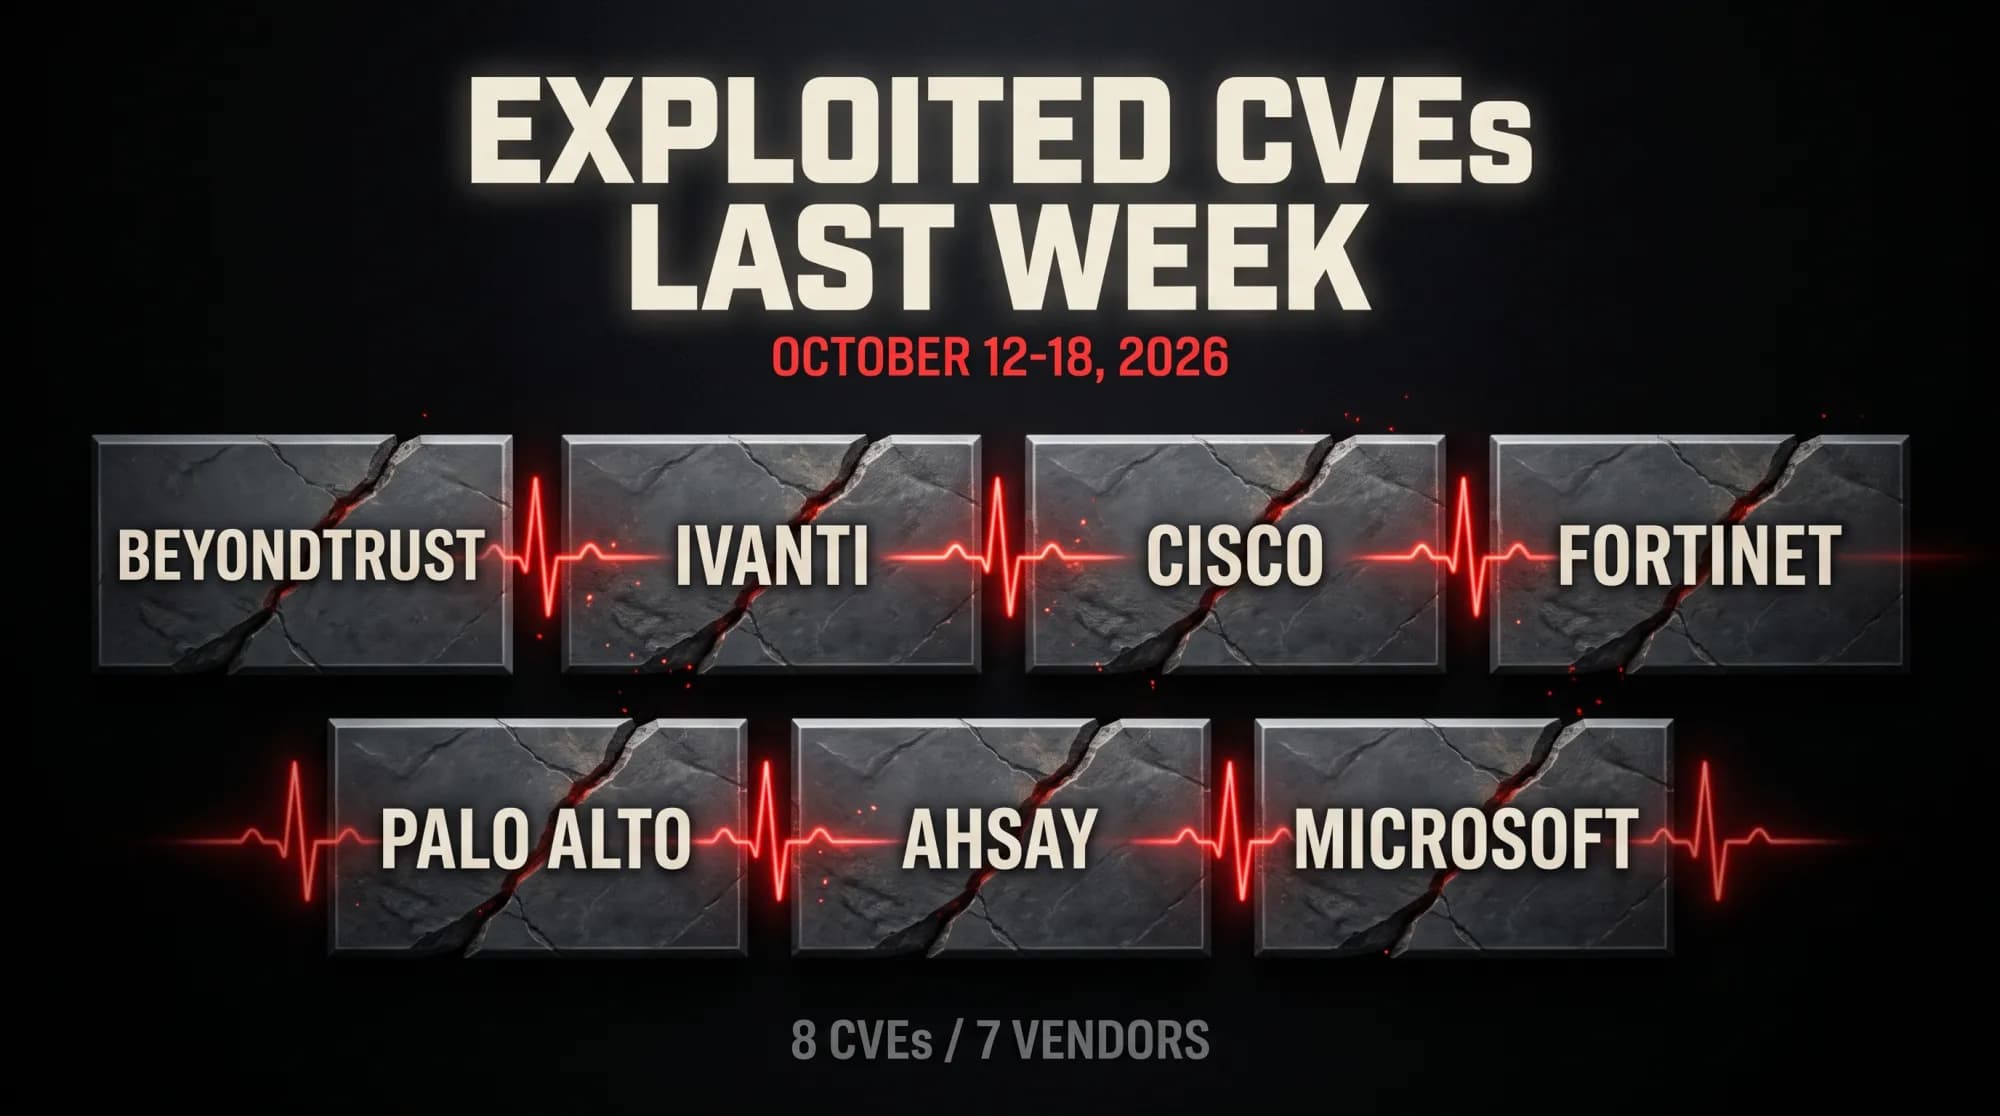
Eight exploited CVEs from seven vendors entered CISA's KEV catalog between October 13 and 16. Five sit on edge or remote access products, seven had an EPSS of 5% or less, and all are marked Active in SSVC. Here is the list, the angle and what to patch first.
CISA added five CVEs to KEV on October 8, all from 2015 to 2023: ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. A joint advisory ties them to a China-linked campaign, and EPSS scores range from 3.6 to 99.5 percent.
Six exploited CVEs reached CISA's KEV catalog between September 29 and October 4, covering Apple, Cisco, Fortinet, Zammad, and NetScaler. Each calls for a different first move, from a simple upgrade to a workaround because no patch exists.
CISA added nine actively exploited CVEs to KEV last week, from F5 and Arista to WordPress, SharePoint, MikroTik, and a fresh pair of Citrix NetScaler zero-days. Here's what happened, and what's still due.
CISA added seven actively exploited vulnerabilities to its KEV catalog in one week, spanning Cisco, Acronis, Google Pixel, and the Linux kernel. Here is what happened, in order, and what is due today.