Topic

CISA KEV

Latest CISA KEV coverage — 27 articles.

Exploited CVEs Oct 26-Nov 1, 2026
Weekly Digest · CISA KEV · Active Exploitation

Exploited CVEs Oct 26-Nov 1, 2026

Nine CVEs from eight vendors joined CISA KEV last week, from a 2.7 VMware logging flaw to a CVSS 10.0 GitLab bug. Same SSVC tags got three-day and 14-day deadlines, so here is what to patch first and why.

9 min read
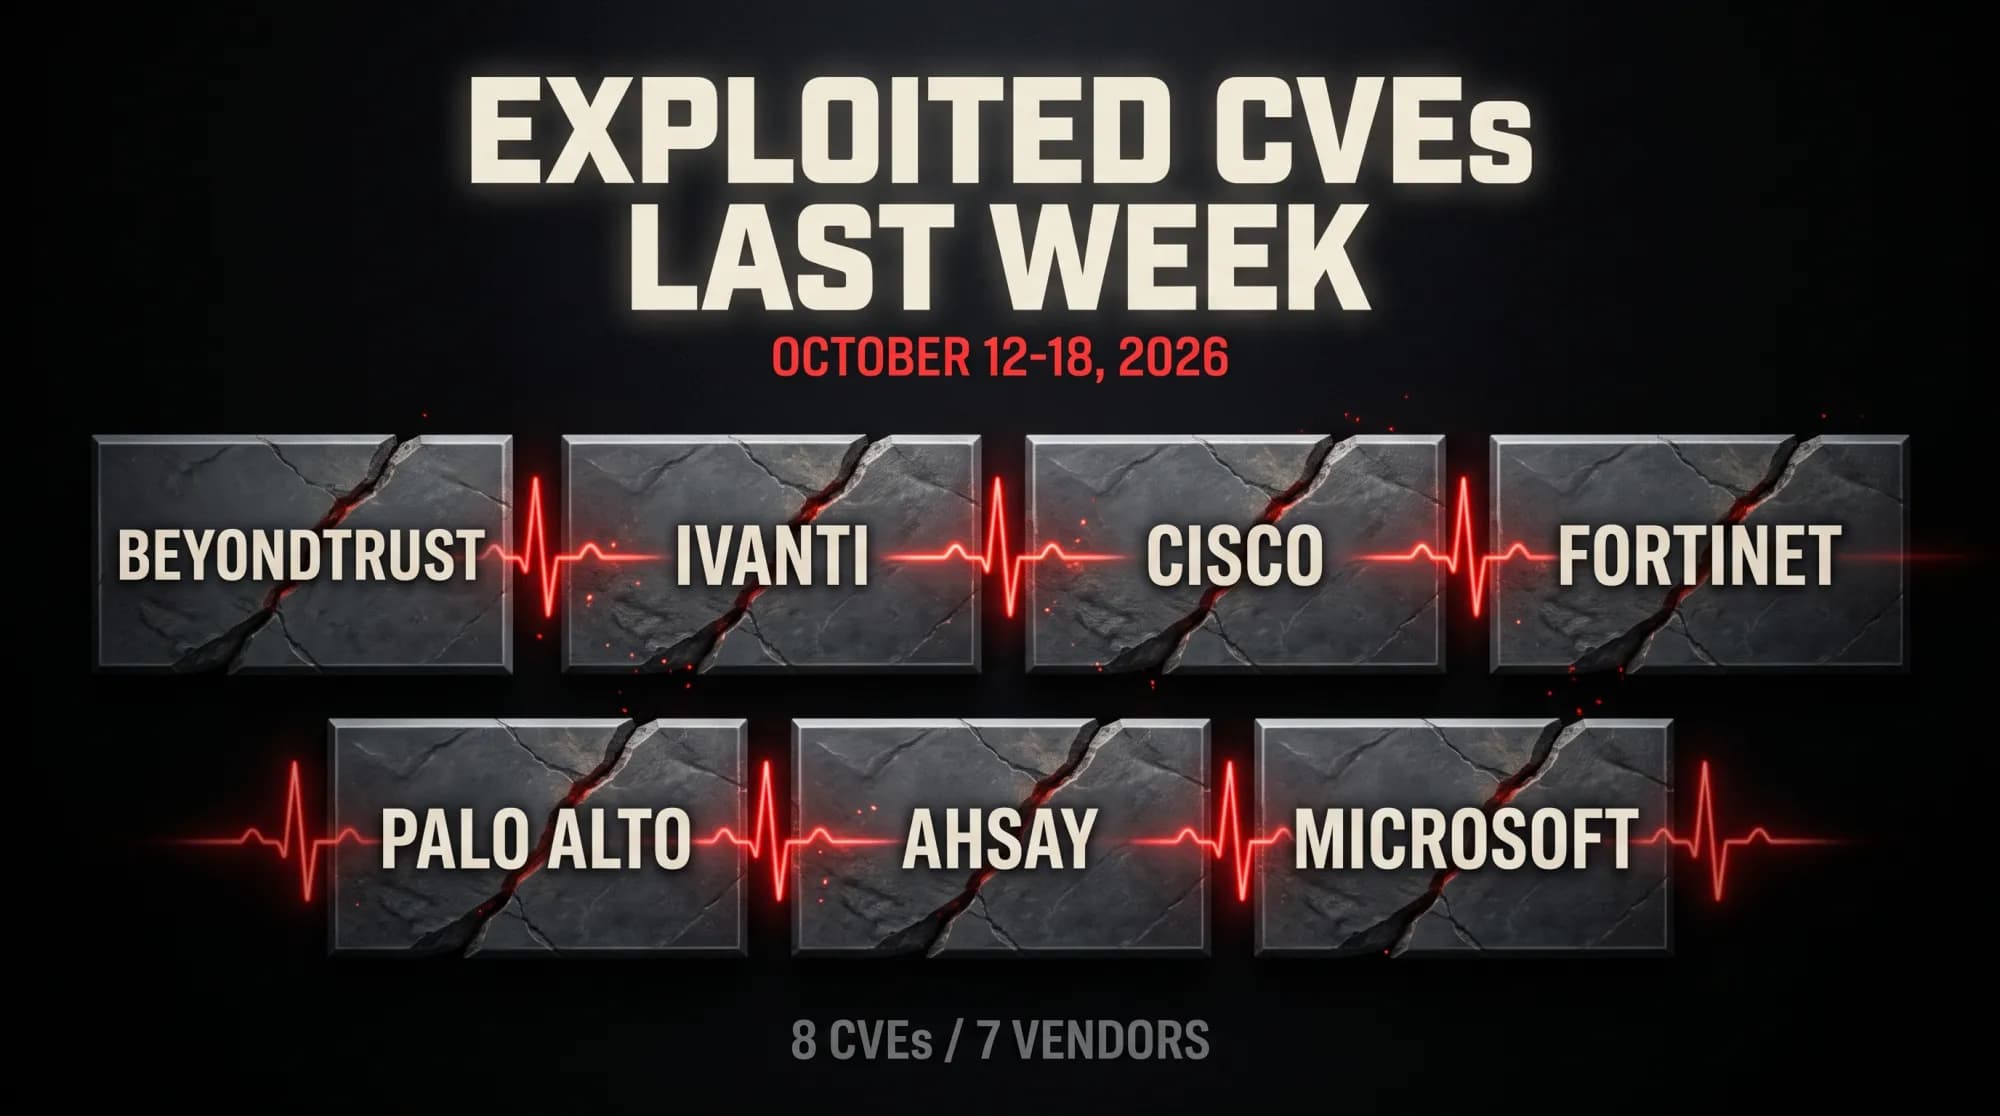
Exploited CVEs Last Week: October 12-18, 2026
Weekly Digest · Active Exploitation · CISA KEV

Exploited CVEs Last Week: October 12-18, 2026

Eight exploited CVEs from seven vendors entered CISA's KEV catalog between October 13 and 16. Five sit on edge or remote access products, seven had an EPSS of 5% or less, and all are marked Active in SSVC. Here is the list, the angle and what to patch first.

6 min read
CVE-2025-61624: PEERSTITCH Malware Abuses a FortiOS Path Traversal Flaw
Fortinet · CISA KEV · Active Exploitation · FortiOS · Malware

CVE-2025-61624: PEERSTITCH Malware Abuses a FortiOS Path Traversal Flaw

Fortinet fixed CVE-2025-61624 in April and rated it Medium. In October, CISA added it to KEV after Unit 42 showed it helping deploy PEERSTITCH, a memory-only implant on FortiGate firewalls. Here are the fixed versions and what to hunt for.

7 min read
Exploited CVEs Last Week: October 5-11, 2026
Active Exploitation · CISA KEV · Weekly Digest

Exploited CVEs Last Week: October 5-11, 2026

CISA added five CVEs to KEV on October 8, all from 2015 to 2023: ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. A joint advisory ties them to a China-linked campaign, and EPSS scores range from 3.6 to 99.5 percent.

5 min read
Exploited CVEs Last Week: September 28-October 4, 2026
Weekly Digest · CISA KEV · Active Exploitation · Apple · Cisco · Citrix · Zammad · Fortinet

Exploited CVEs Last Week: September 28-October 4, 2026

Six exploited CVEs reached CISA's KEV catalog between September 29 and October 4, covering Apple, Cisco, Fortinet, Zammad, and NetScaler. Each calls for a different first move, from a simple upgrade to a workaround because no patch exists.

4 min read
CVE-2026-88771 & CVE-2026-88772: Citrix NetScaler Zero-Days
Zero-Day · CISA KEV · Active Exploitation · Security Alert · Citrix

CVE-2026-88771 & CVE-2026-88772: Citrix NetScaler Zero-Days

Citrix confirmed active exploitation of two NetScaler zero-days, CVE-2026-88771 and CVE-2026-88772, after a weekend of quiet shutdown warnings and NCSC pre-notifications. Here's the mechanism, who's affected, and the September 30 deadline.

5 min read
Exploited CVEs Last Week: September 21-27, 2026
CISA KEV · Active Exploitation · Weekly Digest · Security Alert

Exploited CVEs Last Week: September 21-27, 2026

CISA added nine actively exploited CVEs to KEV last week, from F5 and Arista to WordPress, SharePoint, MikroTik, and a fresh pair of Citrix NetScaler zero-days. Here's what happened, and what's still due.

6 min read
CVE-2026-5430: WSO2's JWT Algorithm Bypass Is Being Exploited for Lateral Movement
CISA KEV · CVE · Active Exploitation · Security Alert · WSO2

CVE-2026-5430: WSO2's JWT Algorithm Bypass Is Being Exploited for Lateral Movement

WatchTowr's honeypot network caught active exploitation of a WSO2 JWT algorithm bypass, with forged tokens granting full access to every backend API a compromised gateway proxies. CISA added it to KEV; federal agencies must patch by September 27.

4 min read
CVE-2026-7273: Nearly 1,000 Zyxel Switches Compromised via a Two-Month-Old Patch
Active Exploitation · CISA KEV · Security Alert · Zyxel

CVE-2026-7273: Nearly 1,000 Zyxel Switches Compromised via a Two-Month-Old Patch

CISA confirmed active exploitation of a Zyxel GS1900 switch vulnerability patched back in June, after GreyNoise found nearly 1,000 compromised devices across 48 countries. Here is the mechanism, who is affected, and what is due by September 24.

4 min read