
CVE-2024-26152
Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
Using label-studio by HumanSignal?
Get instant alerts when new vulnerabilities affect label-studio - before attackers find them.
Description
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 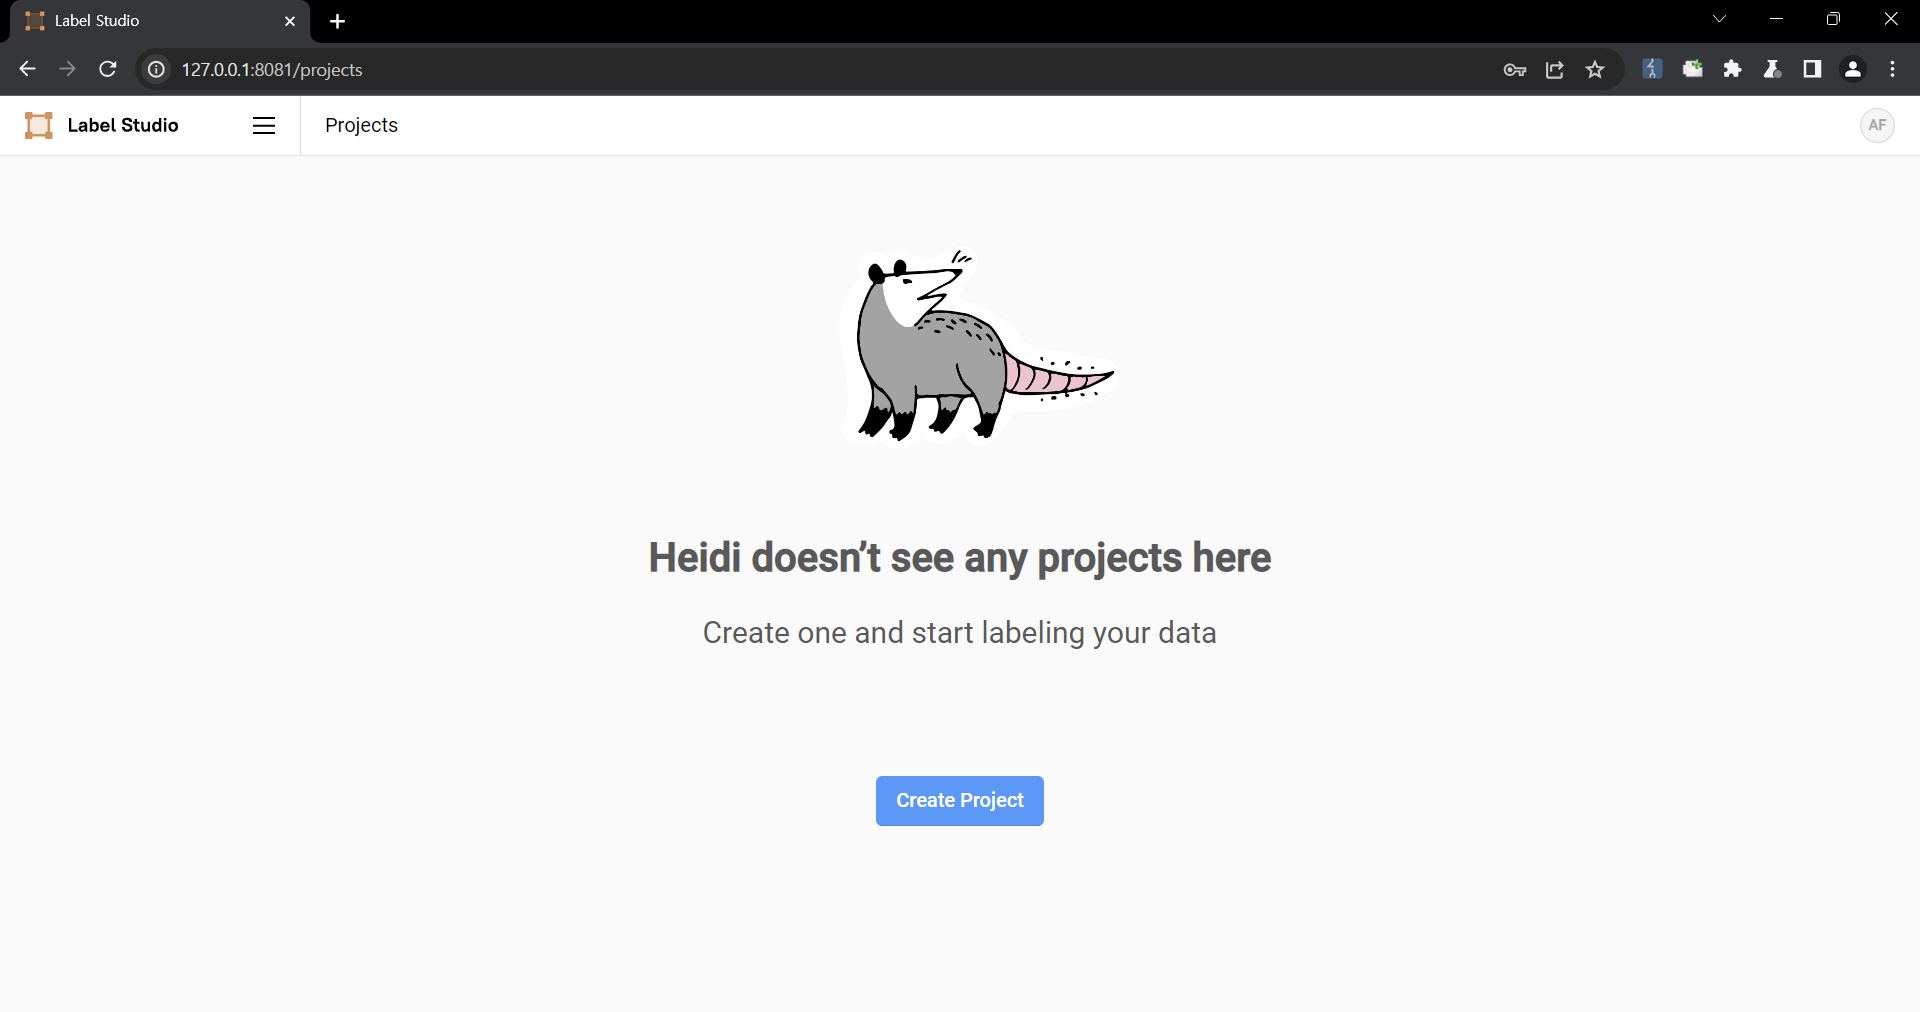 2. Upload a file containing the payload using the "Upload Files" function. 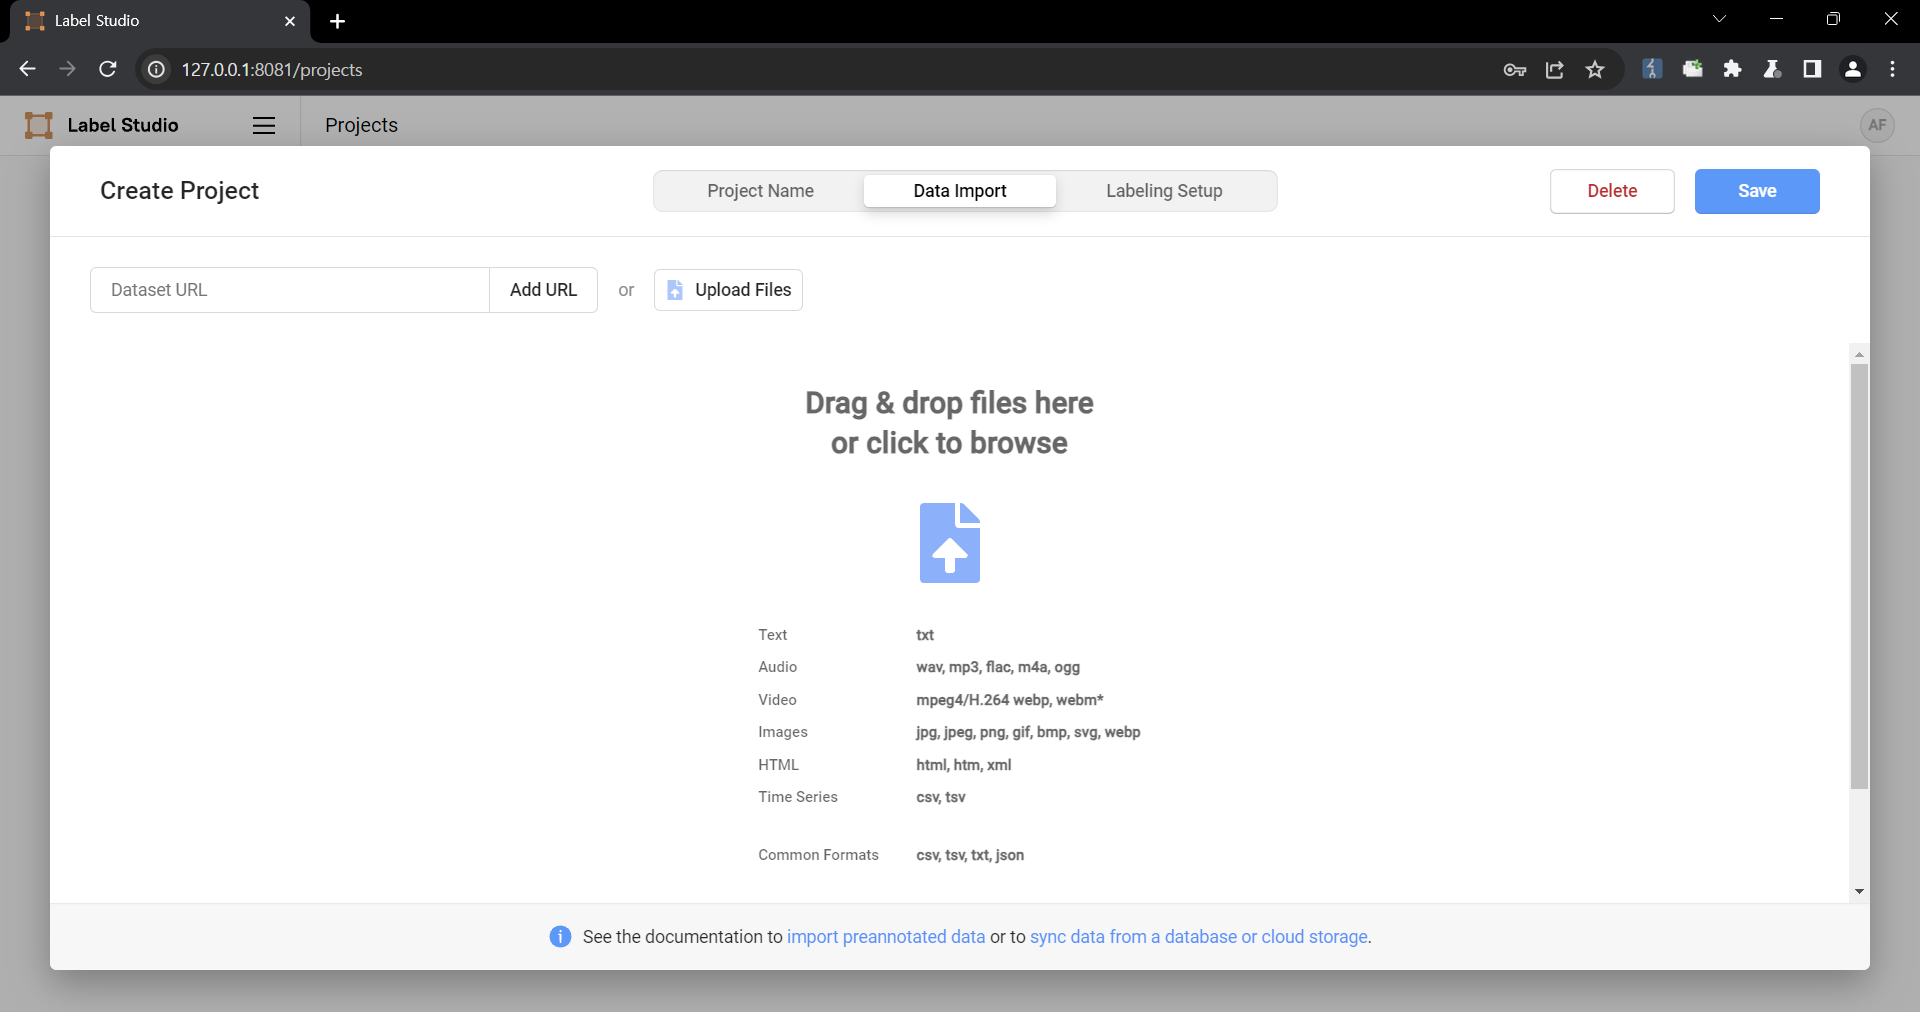 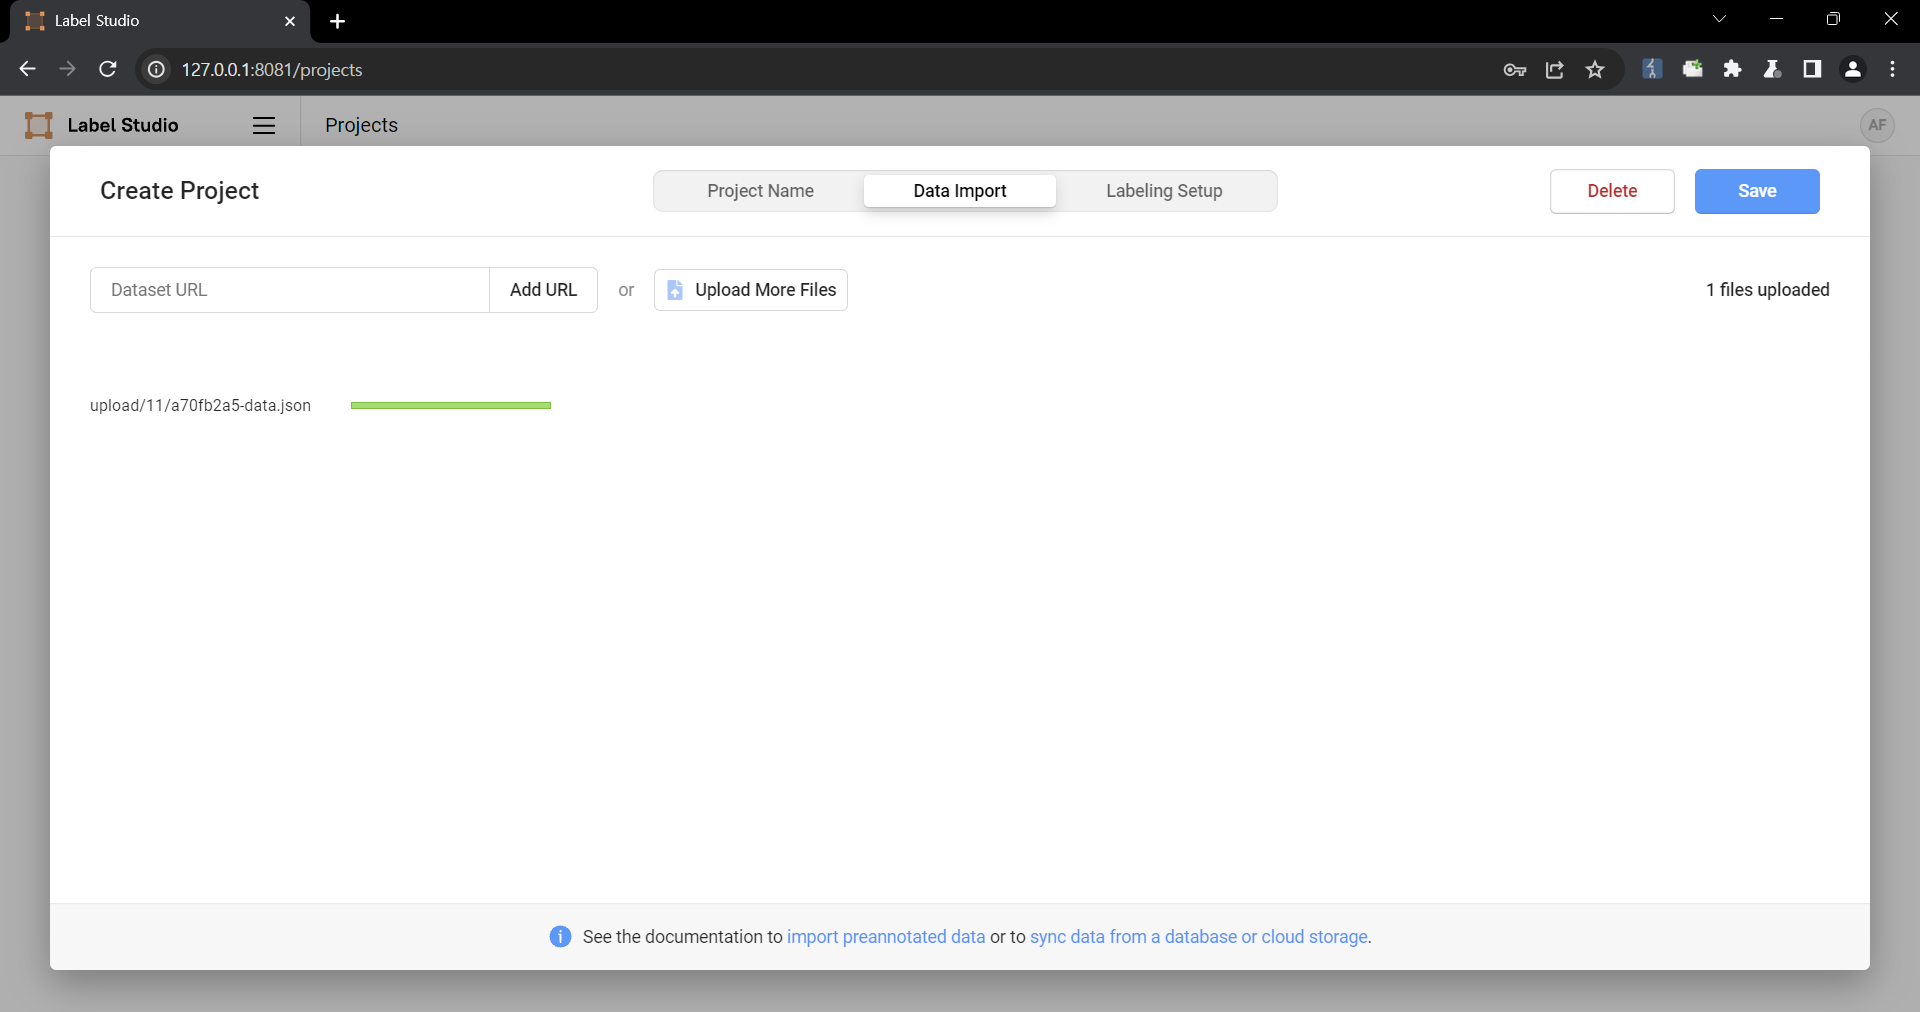 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 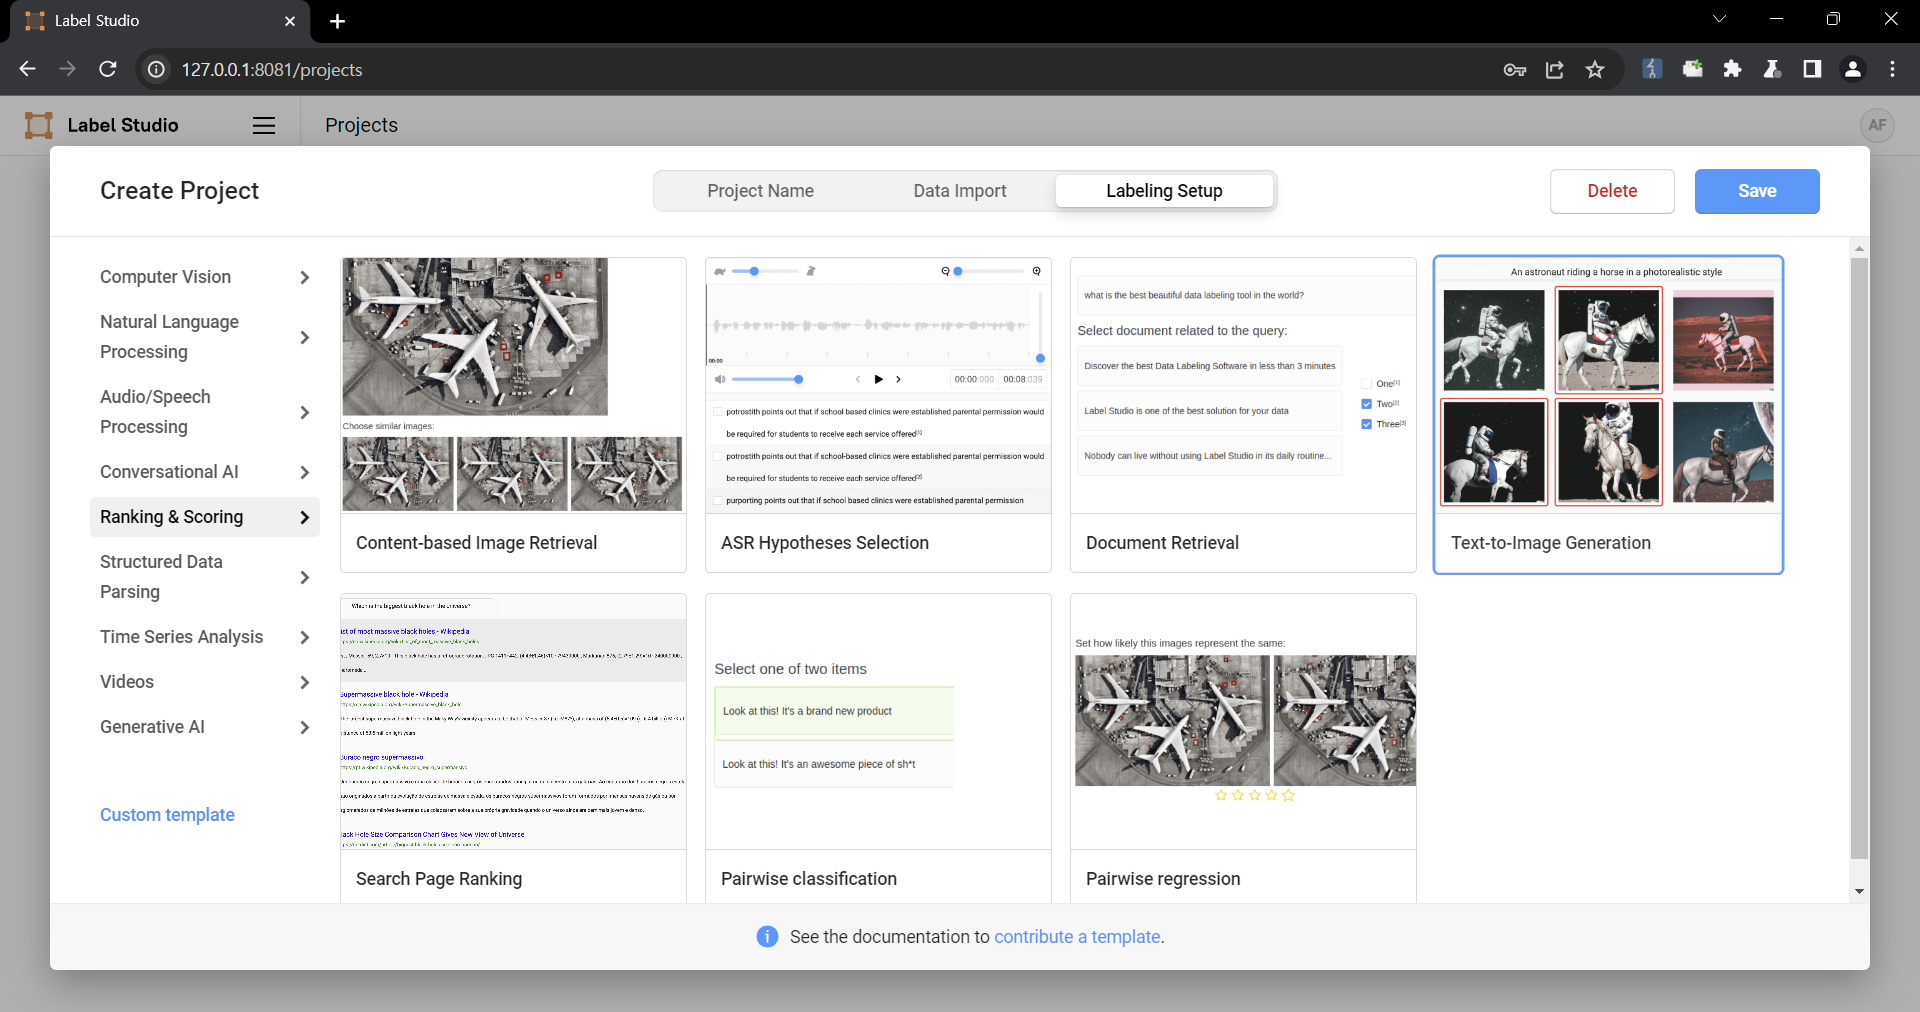 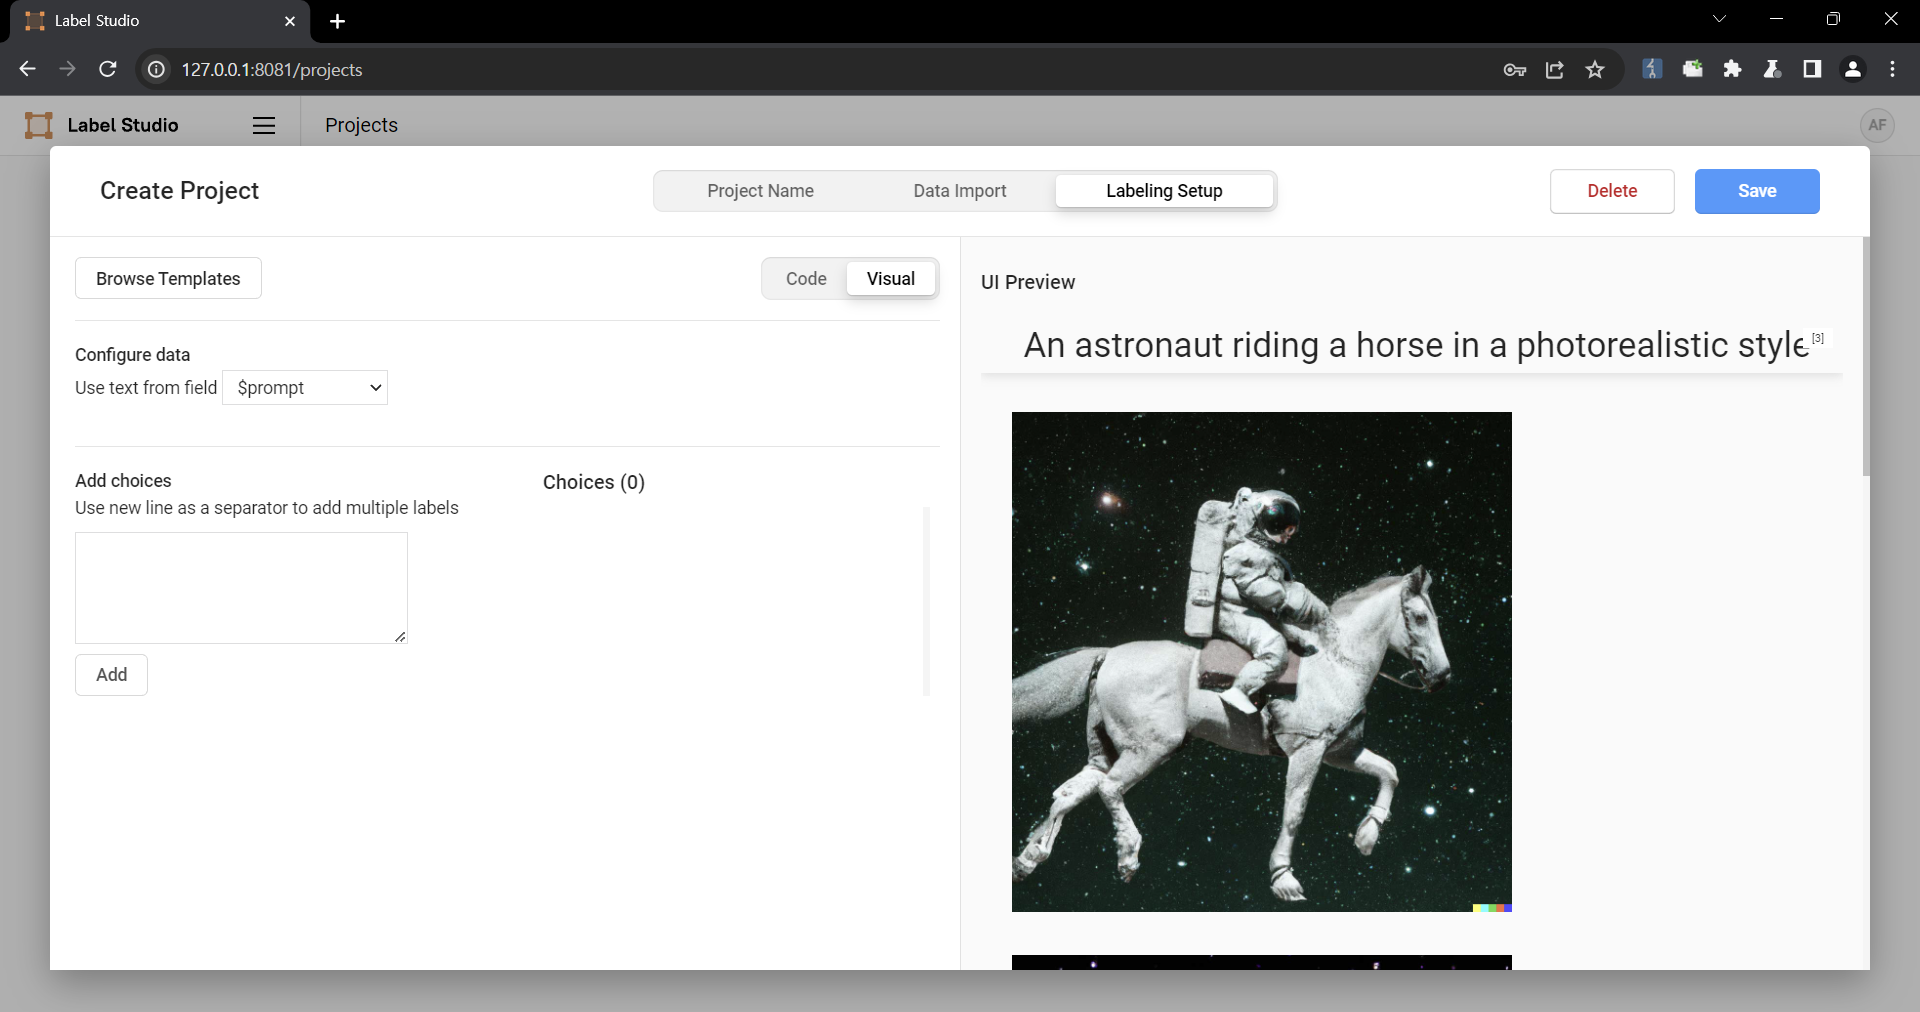 4. Select a task 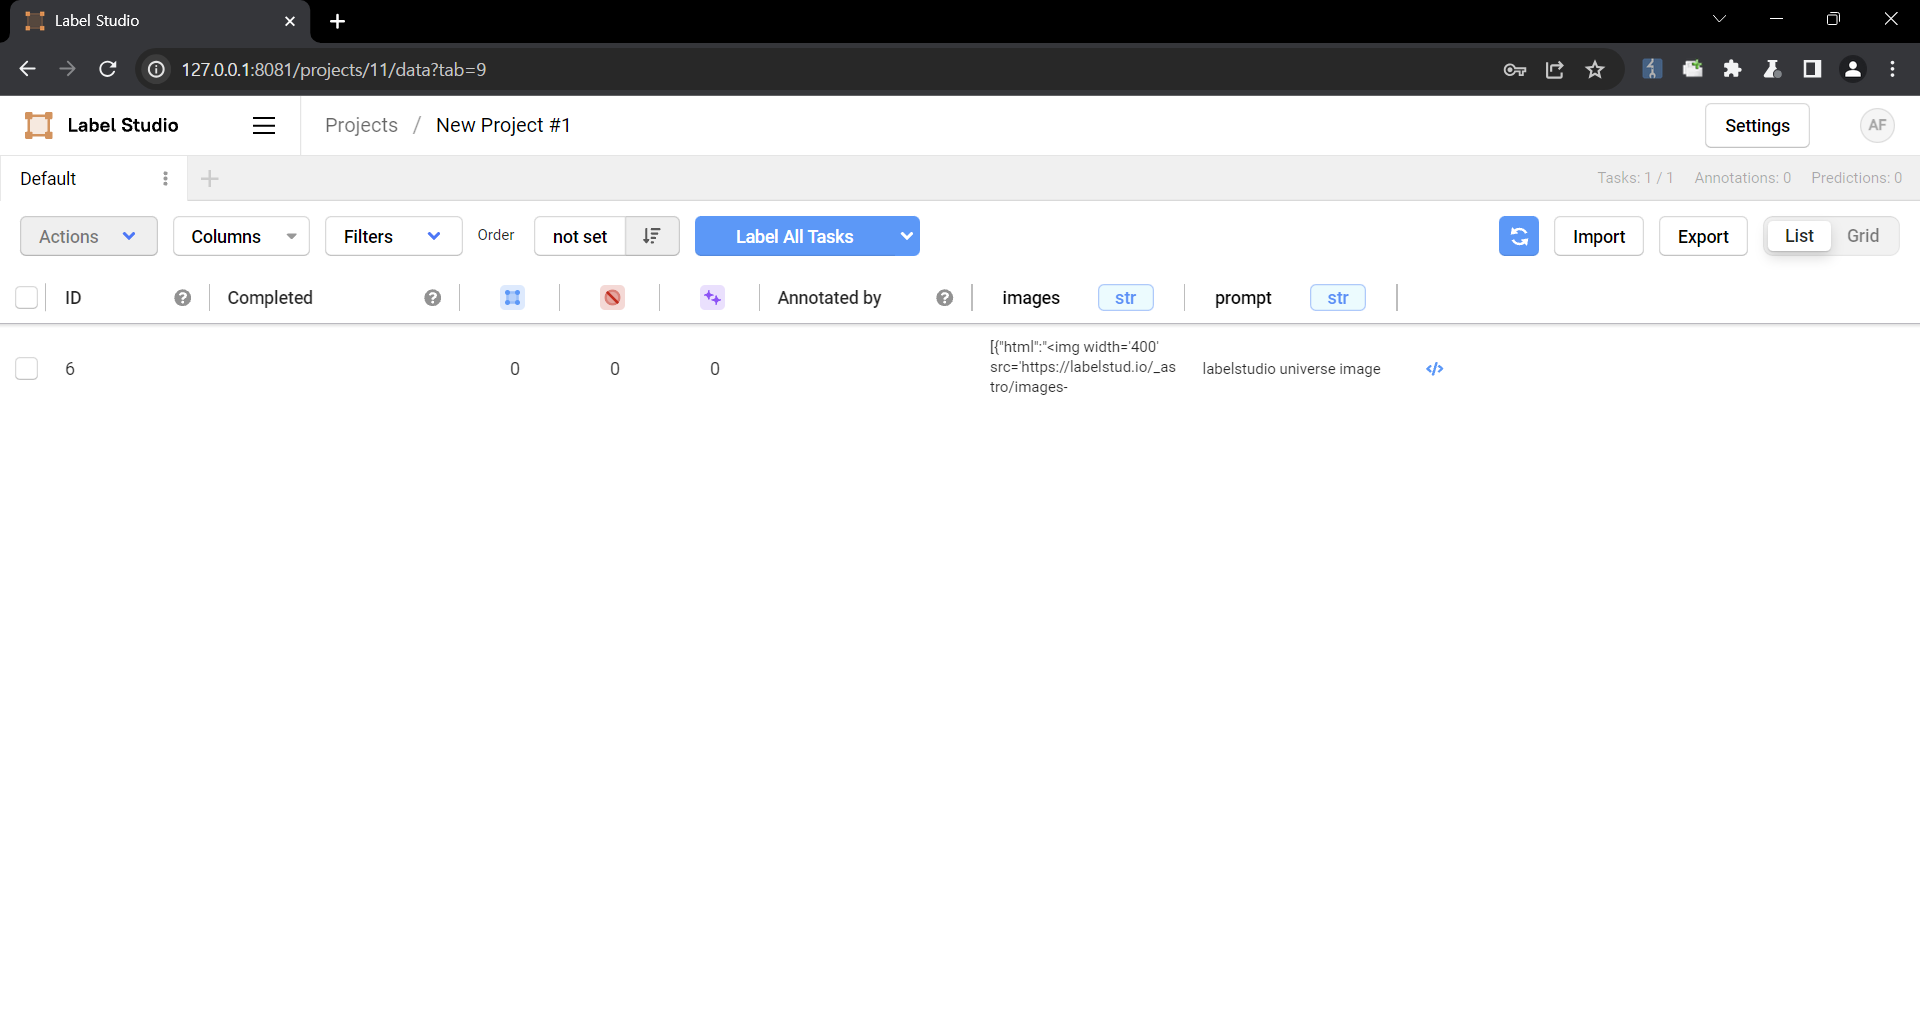 5. Check that the script is running 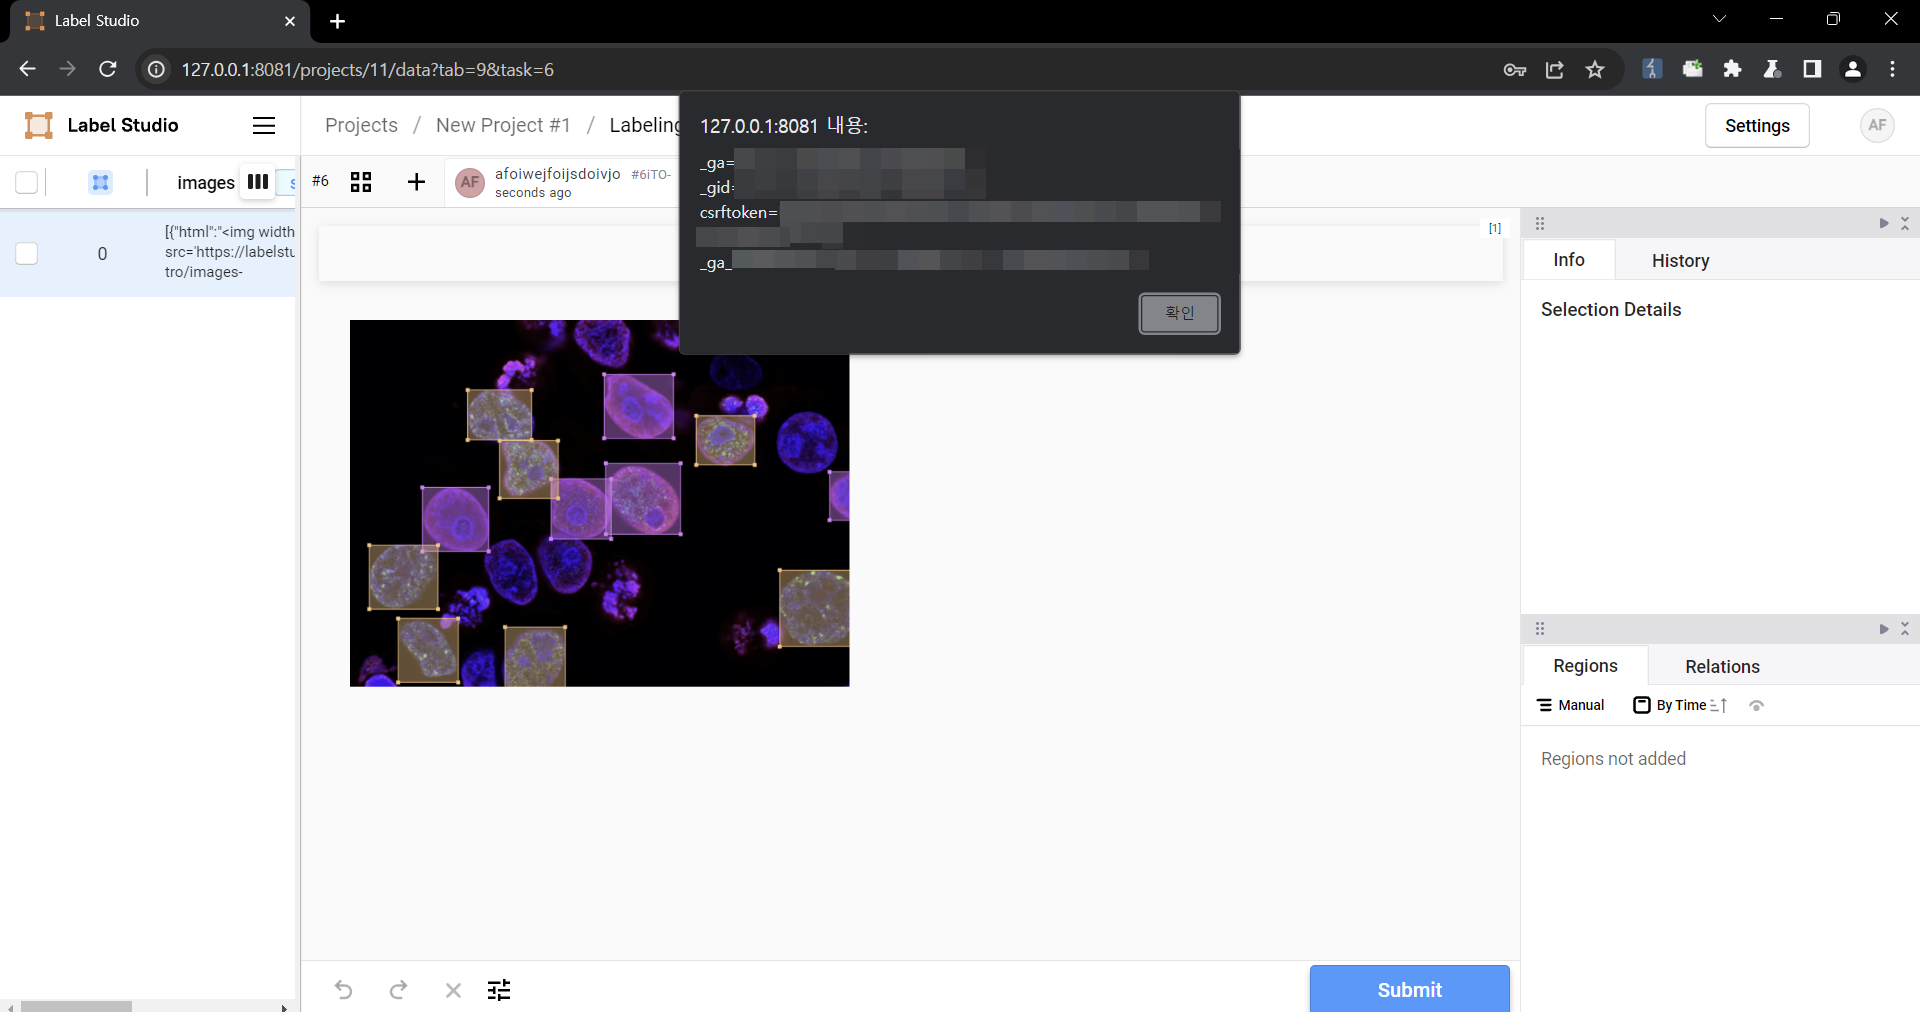 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Affected
Our own answer: ranges merged, affected separated from platform-only, with confidence and review flags.
Remediation
No guide yetNo remediation guidance has been written for this CVE yet. What the record does show:
References (4)
SSVC — Action Prioritization
SSVC signals action urgency (what to patch first), separate from CVSS which measures severity.
CVSS
- Attack Vector
- NETWORK
- Complexity
- LOW
- Privileges
- NONE
- User Interaction
- REQUIRED
- Scope
- CHANGED
- Confidentiality
- LOW
- Integrity
- LOW
- Availability
- NONE
Quick Info
Get alerted
Stop reading CVE feeds looking for your own stack
Track the products you run and VulnTracker tells you when a new CVE affects them — with what is known about fixing it, and nothing about the rest.